
Privacy Policy
Note on the current status (November 2026)
This privacy policy also describes services that we do not currently use. The current situation is as follows:
- Not in use: Google Analytics, Google Ads conversion tracking fonts loaded from Google servers (Google Fonts) and Font Awesome via the Cloudflare CDN. The Josefin Sans and Hanken Grotesk typefaces and all icons are served exclusively from our own server.
- In use: Cookiebot (consent management), Google reCAPTCHA (protection of the contact form) and Google Maps on the contact page. Google Maps is only loaded once you activate the map with a click.
The sections on services that are not in use only apply should we use them again in future; we will update this policy accordingly.
Table of Contents
- Introduction and Overview
- Scope
- Legal Bases
- Contact Details of the Controller
- Storage Period
- Rights under the General Data Protection Regulation
- Data Transfer to Third Countries
- Security of Data Processing
- Communication
- Data Processing Agreement (DPA)
- Cookies
- Web Hosting Introduction
- Web Analytics Introduction
- Social Media Introduction
- Content Delivery Networks Introduction
- Cookie Consent Management Platform Introduction
- External Online Platforms Introduction
- Audio & Video Introduction
- Web Design Introduction
- Online Map Services Introduction
- Content Search Providers Introduction
- Miscellaneous Introduction
- Explanation of Terms Used
- Closing Remarks
Introduction and Overview
We have written this privacy policy (version 26.06.2024-122821163) in order to explain to you, in accordance with the requirements of the General Data Protection Regulation (EU) 2016/679 and applicable national laws, which personal data (data for short) we as the controller – and the processors commissioned by us (e.g. providers) – process, will process in the future, and what lawful options you have. The terms used are to be understood as gender-neutral.
In short: We provide you with comprehensive information about the data we process about you.
Privacy policies usually sound very technical and use legal jargon. This privacy policy, however, is intended to describe the most important things to you as simply and transparently as possible. Insofar as it promotes transparency, technical terms are explained in a reader-friendly way, links to further information are provided and graphics are used. In this way, we inform you in clear and simple language that, in the course of our business activities, we only process personal data if there is a corresponding legal basis. This is certainly not possible if one provides explanations that are as brief, unclear and legalistic-technical as possible, as is often the standard on the internet when it comes to data protection. I hope you find the following explanations interesting and informative, and perhaps there is some information among them that you did not know yet.
If you nevertheless still have questions, we would ask you to contact the responsible body named below or in the legal notice (Impressum), to follow the links provided and to look at further information on third-party sites. You can of course also find our contact details in the legal notice (Impressum).
Scope
This privacy policy applies to all personal data processed by us within the company and to all personal data processed by companies commissioned by us (processors). By personal data, we mean information within the meaning of Art. 4(1) GDPR, such as a person's name, e-mail address and postal address. The processing of personal data ensures that we can offer and invoice our services and products, whether online or offline. The scope of this privacy policy covers:
- all online presences (websites, online shops) that we operate
- social media presences and e-mail communication
- mobile apps for smartphones and other devices
In short: The privacy policy applies to all areas in which personal data is processed in a structured manner within the company via the channels mentioned. Should we enter into legal relationships with you outside of these channels, we will inform you separately if necessary.
Legal Bases
In the following privacy policy, we provide you with transparent information on the legal principles and regulations, i.e. the legal bases of the General Data Protection Regulation, which enable us to process personal data.
As far as EU law is concerned, we refer to REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of 27 April 2016. You can of course read this EU General Data Protection Regulation online on EUR-Lex, the gateway to EU law, at https://eur-lex.europa.eu/legal-content/DE/ALL/?uri=celex%3A32016R0679.
We only process your data if at least one of the following conditions applies:
- Consent (Art. 6(1)(a) GDPR): You have given us your consent to process data for a specific purpose. An example would be the storage of the data you entered in a contact form.
- Contract (Art. 6(1)(b) GDPR): We process your data in order to fulfil a contract or pre-contractual obligations with you. For example, if we conclude a purchase contract with you, we need personal information in advance.
- Legal obligation (Art. 6(1)(c) GDPR): If we are subject to a legal obligation, we process your data. For example, we are legally obliged to retain invoices for accounting purposes. These usually contain personal data.
- Legitimate interests (Art. 6(1)(f) GDPR): In the case of legitimate interests that do not restrict your fundamental rights, we reserve the right to process personal data. For example, we have to process certain data in order to be able to operate our website securely and economically efficiently. This processing is therefore a legitimate interest.
Other conditions, such as the performance of tasks carried out in the public interest and the exercise of official authority, as well as the protection of vital interests, do not generally apply to us. Should such a legal basis nevertheless be relevant, it will be indicated in the appropriate place.
In addition to the EU regulation, national laws also apply:
- In Austria, this is the Federal Act concerning the Protection of Natural Persons with regard to the Processing of Personal Data (Datenschutzgesetz), DSG for short.
- In Germany, the Federal Data Protection Act (Bundesdatenschutzgesetz) applies, BDSG for short.
If further regional or national laws apply, we will inform you about them in the following sections.
Contact Details of the Controller
If you have any questions about data protection or the processing of personal data, you will find the contact details of the responsible person or body below:
ECS Travel Management GmbH
Am Straßfeld 1/Stiege 1/Top 6
2401 Fischamend
E-mail: sa@executivecs.at
Phone: 0664 99654860
Legal notice: https://www.executivecs.at/impressum/
Storage Period
It is a general criterion for us that we only store personal data for as long as is absolutely necessary for the provision of our services and products. This means that we delete personal data as soon as the reason for the data processing no longer exists. In some cases, we are legally obliged to store certain data even after the original purpose has ceased to exist, for example for accounting purposes.
Should you wish your data to be deleted or withdraw your consent to data processing, the data will be deleted as quickly as possible, insofar as there is no obligation to store it.
We will inform you below about the specific duration of the respective data processing, provided we have further information on this.
Rights under the General Data Protection Regulation
In accordance with Articles 13 and 14 GDPR, we inform you of the following rights to which you are entitled, so that data is processed fairly and transparently:
- Under Article 15 GDPR, you have a right of access to information as to whether we process your data. If this is the case, you have the right to receive a copy of the data and to be informed of the following information:
- for what purpose we carry out the processing;
- the categories, i.e. the types of data that are processed;
- who receives this data and, if the data is transferred to third countries, how its security can be guaranteed;
- how long the data is stored;
- the existence of the right to rectification, erasure or restriction of processing and the right to object to processing;
- that you can lodge a complaint with a supervisory authority (links to these authorities can be found below);
- the origin of the data if we have not collected it from you;
- whether profiling is carried out, i.e. whether data is automatically evaluated in order to create a personal profile of you.
- Under Article 16 GDPR, you have the right to rectification of data, which means that we must correct data if you find errors.
- Under Article 17 GDPR, you have the right to erasure (“right to be forgotten”), which specifically means that you may request the deletion of your data.
- Under Article 18 GDPR, you have the right to restriction of processing, which means that we may only store the data but not use it any further.
- Under Article 20 GDPR, you have the right to data portability, which means that, upon request, we will provide you with your data in a commonly used format.
- Under Article 21 GDPR, you have a right to object which, once exercised, results in a change to the processing.
- If the processing of your data is based on Art. 6(1)(e) GDPR (public interest, exercise of official authority) or Art. 6(1)(f) GDPR (legitimate interest), you can object to the processing. We will then check as quickly as possible whether we can legally comply with this objection.
- If data is used for direct advertising, you can object to this type of data processing at any time. We may then no longer use your data for direct marketing.
- If data is used for profiling, you can object to this type of data processing at any time. We may then no longer use your data for profiling.
- Under Article 22 GDPR, you may have the right not to be subject to a decision based solely on automated processing (for example profiling).
- Under Article 77 GDPR, you have the right to lodge a complaint. This means that you can complain to the data protection authority at any time if you believe that the processing of personal data violates the GDPR.
In short: You have rights – do not hesitate to contact the responsible body listed above!
If you believe that the processing of your data violates data protection law or that your data protection rights have been infringed in any other way, you can lodge a complaint with the supervisory authority. For Austria, this is the Data Protection Authority (Datenschutzbehörde), whose website you can find at https://www.dsb.gv.at/. In Germany, there is a data protection officer for each federal state. For more information, you can contact the Federal Commissioner for Data Protection and Freedom of Information (BfDI). The following local data protection authority is responsible for our company:
Austria Data Protection Authority
Head: Dr. Matthias Schmidl
Address: Barichgasse 40-42, 1030 Wien
Phone no.: +43 1 52 152-0
E-mail address: dsb@dsb.gv.at
Website: https://www.dsb.gv.at/
Data Transfer to Third Countries
We only transfer or process data in countries outside the scope of the GDPR (third countries) if you consent to this processing or if there is another legal permission. This applies in particular if the processing is required by law or necessary for the performance of a contractual relationship, and in any case only to the extent that this is generally permitted. In most cases, your consent is the most important reason for us having data processed in third countries. The processing of personal data in third countries such as the USA, where many software manufacturers offer services and have their server locations, may mean that personal data is processed and stored in unexpected ways.
We expressly point out that, according to the opinion of the European Court of Justice, there is currently only an adequate level of protection for data transfers to the USA if a US company that processes personal data of EU citizens in the USA is an active participant in the EU-US Data Privacy Framework. You can find more information on this at: https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en
Data processing by US services that are not active participants in the EU-US Data Privacy Framework may result in data not being processed and stored anonymously. Furthermore, US government authorities may be able to access individual data. In addition, collected data may be linked to data from other services of the same provider, provided you have a corresponding user account. Where possible, we try to use server locations within the EU, if this is offered.
We will inform you in more detail about data transfers to third countries at the appropriate points in this privacy policy, where applicable.
Security of Data Processing
In order to protect personal data, we have implemented both technical and organisational measures. Where possible, we encrypt or pseudonymise personal data. In this way, within the scope of our possibilities, we make it as difficult as possible for third parties to infer personal information from our data.
Art. 25 GDPR speaks here of “data protection by design and by default” and means that security should always be considered and appropriate measures taken for both software (e.g. forms) and hardware (e.g. access to the server room). Below we will, if necessary, go into specific measures.
TLS encryption with https
TLS, encryption and https sound very technical, and they are. We use HTTPS (Hypertext Transfer Protocol Secure, i.e. a “secure hypertext transfer protocol”) to transfer data securely over the internet, protected against eavesdropping.
This means that the entire transfer of all data from your browser to our web server is secured – nobody can “listen in”.
We have thus introduced an additional layer of security and fulfil data protection by design (Article 25(1) GDPR). By using TLS (Transport Layer Security), an encryption protocol for secure data transfer on the internet, we can ensure the protection of confidential data.
You can recognise the use of this data transfer protection by the small lock symbol  at the top left of the browser, to the left of the internet address (e.g. beispielseite.de), and by the use of the https scheme (instead of http) as part of our internet address.
If you would like to know more about encryption, we recommend a Google search for “Hypertext Transfer Protocol Secure wiki” to obtain good links to further information.
Communication
| Communication Summary 👥 Data subjects: Everyone who communicates with us by telephone, e-mail or online form 📓 Data processed: e.g. telephone number, name, e-mail address, form data entered. You can find more details on this under the respective type of contact used 🤝 Purpose: Handling communication with customers, business partners, etc. 📅 Storage period: Duration of the business case and of the statutory requirements ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(b) GDPR (contract), Art. 6(1)(f) GDPR (legitimate interests) |
When you contact us and communicate by telephone, e-mail or online form, personal data may be processed.
The data is processed for the handling and processing of your enquiry and the related business transaction. The data is stored for just as long as this is the case, or for as long as required by law.
Data subjects
All persons who contact us via the communication channels we provide are affected by the processes mentioned.
Telephone
When you call us, the call data is stored in pseudonymised form on the respective end device and with the telecommunications provider used. In addition, data such as name and telephone number may subsequently be sent by e-mail and stored in order to respond to the enquiry. The data is deleted as soon as the business case has been concluded and statutory requirements permit.
When you communicate with us by e-mail, data may be stored on the respective end device (computer, laptop, smartphone, …) and data is stored on the e-mail server. The data is deleted as soon as the business case has been concluded and statutory requirements permit.
Online forms
When you communicate with us via an online form, data is stored on our web server and, where applicable, forwarded to one of our e-mail addresses. The data is deleted as soon as the business case has been concluded and statutory requirements permit.
Legal Bases
The processing of the data is based on the following legal bases:
- Art. 6(1)(a) GDPR (consent): You give us your consent to store your data and to continue to use it for purposes relating to the business case;
- Art. 6(1)(b) GDPR (contract): Processing is necessary for the performance of a contract with you or with a processor such as the telephone provider, or we need to process the data for pre-contractual activities, such as the preparation of an offer;
- Art. 6(1)(f) GDPR (legitimate interests): We want to handle customer enquiries and business communication in a professional manner. For this purpose, certain technical facilities such as e-mail programs, Exchange servers and mobile network operators are necessary in order to be able to conduct communication efficiently.
Data Processing Agreement (DPA)
In this section, we would like to explain to you what a data processing agreement is and why it is needed. Because the term “data processing agreement” is quite a mouthful, we will often use only the acronym DPA in this text. Like most companies, we do not work alone, but also make use of the services of other companies or individuals. By involving various companies or service providers, we may pass on personal data for processing. These partners then act as processors with whom we conclude a contract, the so-called data processing agreement (DPA). The most important thing for you to know is that your personal data is processed exclusively in accordance with our instructions and must be governed by the DPA.
Who are processors?
As a company and website owner, we are responsible for all data that we process from you. In addition to the controllers, there may also be so-called processors. These include any company or person that processes personal data on our behalf. More precisely, and according to the GDPR definition: any natural or legal person, public authority, agency or other body that processes personal data on our behalf is considered a processor. Processors can therefore be service providers such as hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
For a better understanding of the terminology, here is an overview of the three roles in the GDPR:
Data subject (you as a customer or prospective customer) → Controller (we as a company and principal) → Processor (service provider such as a web host or cloud provider)
Content of a data processing agreement
As already mentioned above, we have concluded a DPA with our partners who act as processors. First and foremost, it stipulates that the processor processes the data to be processed exclusively in accordance with the GDPR. The contract must be concluded in writing; however, in this context, an electronically concluded contract is also deemed to be “in writing”. The processing of personal data only takes place on the basis of the contract. The contract must contain the following:
- Commitment to us as the controller
- Obligations and rights of the controller
- Categories of data subjects
- Type of personal data
- Nature and purpose of the data processing
- Subject matter and duration of the data processing
- Location where the data processing is carried out
Furthermore, the contract contains all obligations of the processor. The most important obligations are:
- to ensure data security measures
- to take possible technical and organisational measures to protect the rights of the data subject
- to maintain a record of processing activities
- to cooperate with the data protection supervisory authority upon its request
- to carry out a risk analysis in relation to the personal data received
- sub-processors may only be engaged with the written authorisation of the controller
You can see what such a DPA looks like in practice, for example, at https://www.wko.at/service/wirtschaftsrecht-gewerberecht/eu-dsgvo-mustervertrag-auftragsverarbeitung.html. A model contract is presented there.
Cookies
| Cookies Summary 👥 Data subjects: Visitors to the website 🤝 Purpose: depends on the respective cookie. You can find more details on this below or from the manufacturer of the software that sets the cookie. 📓 Data processed: Depends on the cookie used in each case. You can find more details on this below or from the manufacturer of the software that sets the cookie. 📅 Storage period: depends on the respective cookie, can vary from hours to years ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are cookies?
Our website uses HTTP cookies to store user-specific data.
Below we explain what cookies are and why they are used, so that you can better understand the following privacy policy.
Whenever you surf the internet, you use a browser. Well-known browsers include Chrome, Safari, Firefox, Internet Explorer and Microsoft Edge. Most websites store small text files in your browser. These files are called cookies.
One thing cannot be denied: cookies are really useful little helpers. Almost all websites use cookies. More precisely, they are HTTP cookies, as there are also other cookies for other areas of application. HTTP cookies are small files that are stored on your computer by our website. These cookie files are automatically placed in the cookie folder, effectively the “brain” of your browser. A cookie consists of a name and a value. When defining a cookie, one or more attributes must also be specified.
Cookies store certain user data about you, such as language or personal page settings. When you visit our site again, your browser transmits the “user-related” information back to our site. Thanks to cookies, our website knows who you are and offers you the settings you are used to. In some browsers each cookie has its own file; in others, such as Firefox, all cookies are stored in a single file.
The following graphic shows a possible interaction between a web browser such as Chrome and the web server. The web browser requests a website and receives a cookie back from the server, which the browser uses again as soon as another page is requested.
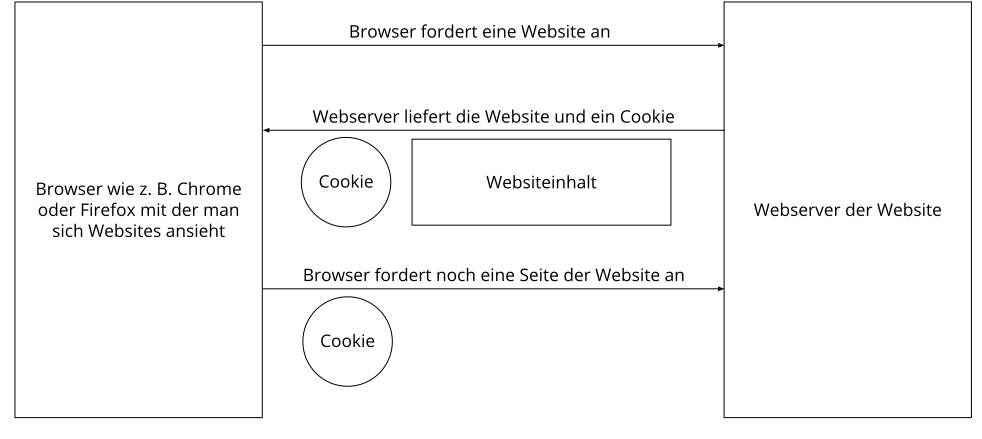
There are both first-party cookies and third-party cookies. First-party cookies are created directly by our site; third-party cookies are created by partner websites (e.g. Google Analytics). Each cookie must be assessed individually, as each cookie stores different data. The expiry time of a cookie also varies from a few minutes to a few years. Cookies are not software programs and do not contain viruses, Trojans or other “pests”. Cookies also cannot access information on your PC.
This is what cookie data can look like, for example:
Name: _ga
Value: GA1.2.1326744211.152122821163-9
Purpose: Differentiation of website visitors
Expiry date: after 2 years
A browser should be able to support these minimum sizes:
- At least 4096 bytes per cookie
- At least 50 cookies per domain
- At least 3000 cookies in total
What types of cookies are there?
The question of which cookies we use in particular depends on the services used and is clarified in the following sections of the privacy policy. At this point, we would like to briefly discuss the different types of HTTP cookies.
There are 4 types of cookies:
Essential cookies
These cookies are necessary to ensure basic functions of the website. For example, these cookies are needed when a user puts a product in the shopping cart, then continues surfing on other pages and only goes to the checkout later. These cookies ensure that the shopping cart is not deleted, even if the user closes their browser window.
Functional cookies
These cookies collect information about user behaviour and whether the user receives any error messages. In addition, these cookies are also used to measure the loading time and the behaviour of the website in different browsers.
Target-oriented cookies
These cookies ensure better user-friendliness. For example, entered locations, font sizes or form data are stored.
Advertising cookies
These cookies are also called targeting cookies. They serve to deliver individually tailored advertising to the user. This can be very practical, but also very annoying.
Usually, when you visit a website for the first time, you are asked which of these types of cookies you would like to allow. And of course this decision is also stored in a cookie.
If you would like to know more about cookies and are not afraid of technical documentation, we recommend https://datatracker.ietf.org/doc/html/rfc6265, the Request for Comments of the Internet Engineering Task Force (IETF) called “HTTP State Management Mechanism”.
Purpose of processing via cookies
Ultimately, the purpose depends on the respective cookie. You can find more details on this below or from the manufacturer of the software that sets the cookie.
What data is processed?
Cookies are small helpers for a wide variety of tasks. Unfortunately, it is not possible to generalise which data are stored in cookies, but we will inform you about the data processed or stored in the following privacy policy.
Storage period of cookies
The storage period depends on the respective cookie and is specified in more detail below. Some cookies are deleted after less than an hour, while others may remain stored on a computer for several years.
You also have an influence on the storage period yourself. You can manually delete all cookies via your browser at any time (see also “Right to object” below). Furthermore, cookies based on consent will be deleted at the latest after you withdraw your consent, without affecting the lawfulness of the storage up to that point.
Right to object – how can I delete cookies?
You decide yourself how and whether you want to use cookies. Regardless of which service or website the cookies originate from, you always have the option of deleting, deactivating or only partially allowing cookies. For example, you can block third-party cookies but allow all other cookies.
If you want to find out which cookies have been stored in your browser, or if you want to change or delete cookie settings, you can find this in your browser settings:
Chrome: Delete, enable and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies to remove data that websites have stored on your computer
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete and manage cookies
If you do not want to have any cookies at all, you can set up your browser so that it always informs you when a cookie is about to be set. This way, you can decide for each individual cookie whether or not to allow it. The procedure differs depending on the browser. The best thing to do is to search for the instructions on Google using the search term “delete cookies Chrome” or “disable cookies Chrome” in the case of a Chrome browser.
Legal basis
The so-called “Cookie Directive” has been in place since 2009. It states that the storage of cookies requires your consent (Art. 6(1)(a) GDPR). Within the EU countries, however, reactions to this directive still vary considerably. In Austria, this directive was implemented in § 165(3) of the Telecommunications Act (2021). In Germany, the Cookie Directive was not implemented as national law. Instead, this directive was largely implemented in § 15(3) of the Telemedia Act (TMG), which has been replaced by the Digital Services Act (DDG) since May 2024.
For strictly necessary cookies, even where no consent has been given, there are legitimate interests (Art. 6(1)(f) GDPR), which in most cases are of an economic nature. We want to provide visitors to the website with a pleasant user experience, and certain cookies are often strictly necessary for this.
Insofar as cookies that are not strictly necessary are used, this only happens with your consent. In this respect, the legal basis is Art. 6(1)(a) GDPR.
In the following sections, you will be informed in more detail about the use of cookies, insofar as the software used makes use of cookies.
Web hosting introduction
| Web hosting summary 👥 Data subjects: website visitors 🤝 Purpose: professional hosting of the website and securing its operation 📓 Data processed: IP address, time of the website visit, browser used and other data. You can find more details on this further below or from the respective web hosting provider used. 📅 Storage period: depends on the respective provider, but generally 2 weeks ⚖️ Legal bases: Art. 6(1)(f) GDPR (legitimate interests) |
What is web hosting?
When you visit websites nowadays, certain information – including personal data – is automatically created and stored, and this is also the case on this website. These data should be processed as sparingly as possible and only with justification. By website, incidentally, we mean the entirety of all web pages on a domain, i.e. everything from the start page (homepage) to the very last subpage (like this one). By domain we mean, for example, example.com or sampleexample.com.
When you want to view a website on a computer, tablet or smartphone, you use a program called a web browser. You probably know some web browsers by name: Google Chrome, Microsoft Edge, Mozilla Firefox and Apple Safari. We simply refer to them as browsers or web browsers.
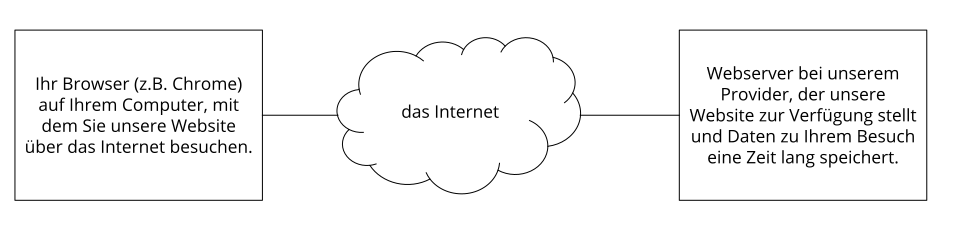
In order to display the website, the browser has to connect to another computer where the website's code is stored: the web server. Operating a web server is a complicated and demanding task, which is why it is usually taken over by professional service providers, the providers. They offer web hosting and thus ensure reliable and error-free storage of website data. That is a lot of technical terms, but please stay with us, it gets even better!
Personal data may be processed when the browser on your computer (desktop, laptop, tablet or smartphone) establishes a connection and during the data transfer to and from the web server. On the one hand, your computer stores data; on the other hand, the web server must also store data for a certain period of time in order to ensure proper operation.
A picture is worth a thousand words, so the following graphic illustrates the interaction between the browser, the internet and the hosting provider.
Why do we process personal data?
The purposes of the data processing are:
- Professional hosting of the website and securing its operation
- to maintain operational and IT security
- Anonymous evaluation of access behaviour to improve our offering and, where applicable, for criminal prosecution or the pursuit of claims
What data is processed?
Even while you are visiting our website right now, our web server – that is the computer on which this website is stored – usually automatically stores data such as
- the complete internet address (URL) of the web page accessed
- browser and browser version (e.g. Chrome 87)
- the operating system used (e.g. Windows 10)
- the address (URL) of the previously visited page (referrer URL) (e.g. https://www.beispielquellsite.de/vondabinichgekommen/)
- the host name and the IP address of the device from which the website is accessed (e.g. COMPUTERNAME and 194.23.43.121)
- date and time
- in files, the so-called web server log files
How long are data stored?
As a rule, the data mentioned above are stored for two weeks and then automatically deleted. We do not pass on these data, but we cannot rule out that these data may be viewed by authorities in the event of unlawful conduct.
In short: Your visit is logged by our provider (the company that runs our website on special computers (servers)), but we do not pass on your data without your consent!
Legal basis
The lawfulness of the processing of personal data in the context of web hosting results from Art. 6(1)(f) GDPR (safeguarding of legitimate interests), as the use of professional hosting with a provider is necessary in order to present the company on the internet in a secure and user-friendly manner and to be able to pursue attacks and claims arising from this, if necessary.
As a rule, there is a data processing agreement between us and the hosting provider pursuant to Art. 28 et seq. GDPR, which ensures compliance with data protection and guarantees data security.
External web hosting provider privacy policy
Below you will find the contact details of our external hosting provider, where, in addition to the information above, you can find out more about the data processing:
VPS hoster name:
Company name: CKStudio e.U.
Address: Webgasse 43/3D, 1060 Wien
Contact: info@ckstudio.at
Actual hosting provider:
easyname GmbH Canettistraße 5/10, 1100 Wien, Österreich
E-mail address: office@easyname.com
Phone: 01 353 2222
You can find out more about the data processing by this provider in the privacy policy.
Web analytics introduction
| Web analytics privacy policy summary 👥 Data subjects: website visitors 🤝 Purpose: evaluation of visitor information to optimise the web offering. 📓 Data processed: access statistics containing data such as access locations, device data, access duration and time, navigation behaviour, click behaviour and IP addresses. You can find more details on this from the respective web analytics tool used. 📅 Storage period: depends on the web analytics tool used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is web analytics?
On our website we use software to evaluate the behaviour of website visitors, known as web analytics or web analysis for short. In the process, data are collected which the respective analytics tool provider (also called a tracking tool) stores, manages and processes. With the help of these data, analyses of user behaviour on our website are created and made available to us as the website operator. In addition, most tools offer various testing options. For example, we can test which offers or content are best received by our visitors. To do this, we show you two different offers for a limited period of time. After the test (a so-called A/B test), we know which product or which content our website visitors find more interesting. For such test procedures, as well as for other analytics procedures, user profiles may also be created and the data stored in cookies.
Why do we use web analytics?
We have a clear goal in mind with our website: we want to deliver the best web offering on the market for our industry. To achieve this goal, we want, on the one hand, to provide the best and most interesting offering and, on the other hand, to make sure that you feel completely at ease on our website. With the help of web analytics tools, we can take a closer look at the behaviour of our website visitors and then improve our web offering accordingly for you and for us. For example, we can see the average age of our visitors, where they come from, when our website is visited most or which content or products are particularly popular. All this information helps us to optimise the website and thus adapt it as well as possible to your needs, interests and wishes.
What data is processed?
Exactly which data are stored naturally depends on the analytics tools used. As a rule, however, data such as which content you view on our website, which buttons or links you click, when you access a page, which browser you use, which device (PC, tablet, smartphone, etc.) you use to visit the website or which computer system you use are stored. If you have agreed that location data may also be collected, these may also be processed by the web analytics tool provider.
Your IP address is also stored. According to the General Data Protection Regulation (GDPR), IP addresses are personal data. However, your IP address is usually stored in pseudonymised form (i.e. in an unrecognisable and shortened form). For the purposes of testing, web analysis and web optimisation, no direct data such as your name, age, address or e-mail address are generally stored. All these data, if collected, are stored in pseudonymised form. This means that you cannot be identified as a person.
The following example shows schematically how Google Analytics works as an example of client-based web tracking with JavaScript code.
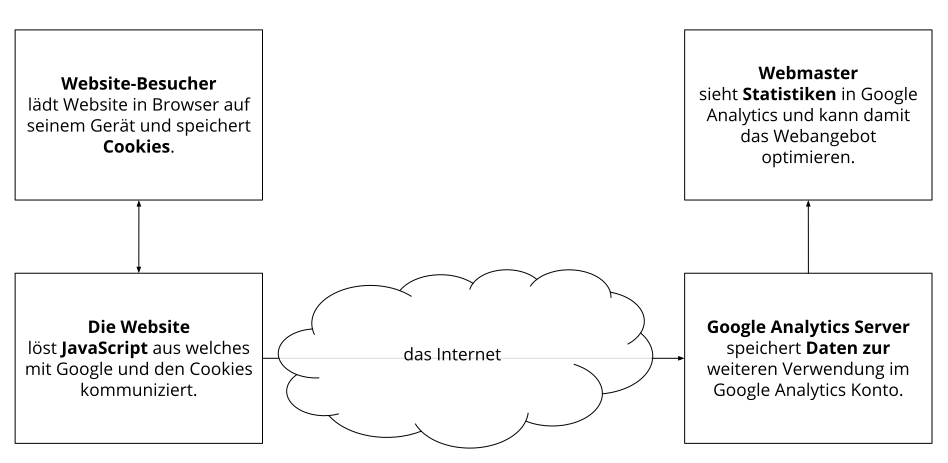
How long the respective data are stored always depends on the provider. Some cookies only store data for a few minutes or until you leave the website again, while other cookies can store data for several years.
Duration of data processing
We inform you below about the duration of the data processing, insofar as we have further information on this. In general, we only process personal data for as long as is strictly necessary to provide our services and products. Where required by law, for example in the case of accounting, this storage period may also be exceeded.
Right to object
You also have the right and the option to withdraw your consent to the use of cookies or third-party providers at any time. This can be done either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser.
Legal basis
The use of web analytics requires your consent, which we have obtained with our cookie pop-up. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur during collection by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offering technically and economically. With the help of web analytics, we can detect errors on the website, identify attacks and improve cost-effectiveness. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tools insofar as you have given your consent.
Since cookies are used with web analytics tools, we also recommend that you read our general privacy policy on cookies. To find out exactly which of your data are stored and processed, you should read the privacy policies of the respective tools.
Information on specific web analytics tools – where available – can be found in the following sections.
Google Analytics privacy policy
| Google Analytics privacy policy summary 👥 Data subjects: website visitors 🤝 Purpose: evaluation of visitor information to optimise the web offering. 📓 Data processed: access statistics containing data such as access locations, device data, access duration and time, navigation behaviour and click behaviour. You can find more details on this further below in this privacy policy. 📅 Storage period: individually configurable; by default, Google Analytics 4 stores data for 14 months ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Analytics?
On our website we use the analytics tracking tool Google Analytics in the version Google Analytics 4 (GA4) of the American company Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. Google Analytics collects data about your actions on our website. Through the combination of various technologies such as cookies, device IDs and login information, however, you as a user can be identified across different devices. As a result, your actions can also be analysed across platforms.
For example, when you click on a link, this event is stored in a cookie and sent to Google Analytics. With the help of the reports we receive from Google Analytics, we can better adapt our website and our service to your wishes. In the following, we go into more detail about the tracking tool and, above all, inform you about which data are processed and how you can prevent this.
Google Analytics is a tracking tool used to analyse the traffic on our website. The basis of these measurements and analyses is a pseudonymous user identification number. This number does not contain any personal data such as name or address, but serves to assign events to an end device. GA4 uses an event-based model that captures detailed information on user interactions such as page views, clicks, scrolling and conversion events. In addition, various machine learning functions have been built into GA4 in order to better understand user behaviour and certain trends. With the help of machine learning functions, GA4 relies on modelling. This means that, on the basis of the data collected, missing data can also be extrapolated in order to optimise the analysis and also to be able to make forecasts.
In order for Google Analytics to work at all, a tracking code is built into the code of our website. When you visit our website, this code records various events that you perform on our website. With the event-based data model of GA4, we as website operators can define and track specific events in order to obtain analyses of user interactions. Thus, in addition to general information such as clicks or page views, special events that are important for our business can also be tracked. Such special events can be, for example, the submission of a contact form or the purchase of a product.
As soon as you leave our website, these data are sent to the Google Analytics servers and stored there.
Google processes the data and we receive reports on your user behaviour. These may include, among others, the following reports:
- Audience reports: Through audience reports we get to know our users better and know more precisely who is interested in our service.
- Advertising reports: Advertising reports make it easier for us to analyse and improve our online advertising.
- Acquisition reports: Acquisition reports give us helpful information on how we can get more people excited about our service.
- Behaviour reports: Here we learn how you interact with our website. We can trace the path you take on our site and which links you click.
- Conversion reports: A conversion is a process in which you perform a desired action as a result of a marketing message. For example, when you go from being a mere website visitor to a buyer or newsletter subscriber. With the help of these reports, we learn more about how our marketing measures are received by you. In this way, we aim to increase our conversion rate.
- Real-time reports: Here we always find out immediately what is currently happening on our website. For example, we can see how many users are reading this text right now.
In addition to the analysis reports mentioned above, Google Analytics 4 also offers the following functions, among others:
- Event-based data model: This model captures very specific events that can take place on our website. For example, playing a video, purchasing a product or signing up for our newsletter.
- Advanced analysis functions: With these functions we can understand your behaviour on our website or certain general trends even better. For example, we can segment user groups, carry out comparative analyses of target groups or trace your route or path on our website.
- Predictive modelling: On the basis of collected data, missing data can be extrapolated through machine learning to predict future events and trends. This can help us to develop better marketing strategies.
- Cross-platform analysis: The collection and analysis of data are possible from both websites and apps. This gives us the opportunity to analyse user behaviour across platforms, provided, of course, that you have consented to the data processing.
Why do we use Google Analytics on our website?
Our goal with this website is clear: we want to offer you the best possible service. The statistics and data from Google Analytics help us to achieve this goal.
The statistically evaluated data give us a clear picture of the strengths and weaknesses of our website. On the one hand, we can optimise our site so that it is more easily found on Google by interested people. On the other hand, the data help us to better understand you as a visitor. We therefore know very precisely what we need to improve on our website in order to offer you the best possible service. The data also help us to carry out our advertising and marketing measures in a more individual and cost-effective way. After all, it only makes sense to show our products and services to people who are interested in them.
Which data are stored by Google Analytics?
Using a tracking code, Google Analytics creates a random, unique ID that is linked to your browser cookie. This is how Google Analytics recognises you as a new user, and a user ID is assigned to you. The next time you visit our site, you will be recognised as a “returning” user. All data collected are stored together with this user ID. Only this makes it possible to evaluate pseudonymous user profiles.
In order to be able to analyse our website with Google Analytics, a property ID must be inserted into the tracking code. The data are then stored in the corresponding property. The Google Analytics 4 property is the default for every newly created property. Depending on the property used, data are stored for different lengths of time.
Through identifiers such as cookies, app instance IDs, user IDs or custom event parameters, your interactions are measured across platforms, provided you have given your consent. Interactions are all kinds of actions that you perform on our website. If you also use other Google systems (such as a Google account), data generated via Google Analytics may be linked with third-party cookies. Google does not pass on any Google Analytics data unless we as the website operator authorise this. Exceptions may occur if required by law.
According to Google, no IP addresses are logged or stored in Google Analytics 4. However, Google uses the IP address data to derive location data and deletes them immediately afterwards. All IP addresses collected from users in the EU are therefore deleted before the data are stored in a data centre or on a server.
Since the focus of Google Analytics 4 is on event-based data, the tool uses significantly fewer cookies compared to earlier versions (such as Google Universal Analytics). Nevertheless, there are some specific cookies that are used by GA4. These include, for example:
Name: _ga
Value: 2.1326744211.152122821163-5
Purpose: By default, analytics.js uses the _ga cookie to store the user ID. Basically, it serves to distinguish between website visitors.
Expiry date: after 2 years
Name: _gid
Value: 2.1687193234.152122821163-1
Purpose: This cookie also serves to distinguish between website visitors
Expiry date: after 24 hours
Name: _gat_gtag_UA_<property-id>
Value: 1
Purpose: Used to throttle the request rate. If Google Analytics is provided via Google Tag Manager, this cookie is named _dc_gtm_ <property-id>.
Expiry date: after 1 minute
Note: This list cannot claim to be complete, as Google repeatedly changes its choice of cookies. One aim of GA4 is also to improve data protection. The tool therefore offers several options for controlling data collection. For example, we can set the storage period ourselves and also control data collection.
Here we show you an overview of the most important types of data collected with Google Analytics:
Heatmaps: Google creates so-called heatmaps. Heatmaps show exactly those areas that you click on. This gives us information about where you are “moving around” on our site.
Session duration: Google defines session duration as the time you spend on our site without leaving it. If you have been inactive for 20 minutes, the session ends automatically.
Bounce rate (German: Absprungrate): A bounce occurs when you view only one page on our website and then leave our website again.
Account creation: If you create an account or place an order on our website, Google Analytics collects these data.
Location: IP addresses are not logged or stored in Google Analytics. However, shortly before the IP address is deleted, derivations are used for location data.
Technical information: Technical information includes, among other things, your browser type, your internet service provider or your screen resolution.
Source of origin: Google Analytics, and of course we too, are interested in which website or which advertisement brought you to our site.
Other data include contact details, any ratings, the playing of media (e.g. when you play a video via our site), the sharing of content via social media or adding to your favourites. This list does not claim to be complete and serves only as a general guide to data storage by Google Analytics.
How long and where are the data stored?
Google has its servers distributed all over the world. Here you can read exactly where the Google data centres are located: https://www.google.com/about/datacenters/locations/?hl=de
Your data are distributed across various physical storage media. This has the advantage that the data can be retrieved more quickly and are better protected against manipulation. Every Google data centre has corresponding emergency programmes for your data. If, for example, hardware at Google fails or natural disasters paralyse servers, the risk of a service interruption at Google nevertheless remains low.
The retention period of the data depends on the properties used. The storage period is always set separately for each individual property. Google Analytics offers us four options for controlling the storage period:
- 2 months: this is the shortest storage period.
- 14 months: by default, data remain stored in GA4 for 14 months.
- 26 months: data can also be stored for 26 months.
- Data are only deleted when we delete them manually
In addition, there is also the option that data are only deleted if you no longer visit our website within the period we have chosen. In this case, the retention period is reset each time you visit our website again within the specified period.
Once the specified period has expired, the data are deleted once a month. This retention period applies to your data linked to cookies, user recognition and advertising IDs (e.g. cookies of the DoubleClick domain). Report results are based on aggregated data and are stored independently of user data. Aggregated data are a merging of individual data into a larger unit.
How can I delete my data or prevent data storage?
Under the data protection law of the European Union, you have the right to obtain information about your data and to update, delete or restrict them. With the help of the browser add-on for deactivating Google Analytics JavaScript (analytics.js, gtag.js), you prevent Google Analytics 4 from using your data. You can download and install the browser add-on at https://tools.google.com/dlpage/gaoptout?hl=de. Please note that this add-on only deactivates data collection by Google Analytics.
If you generally wish to deactivate, delete or manage cookies, you will find the relevant links to the respective instructions for the most popular browsers in the section “Cookies”.
Legal basis
The use of Google Analytics requires your consent, which we have obtained with our cookie popup. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data, as may occur when data is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offering technically and economically. With the help of Google Analytics, we detect website errors, can identify attacks and improve economic efficiency. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Analytics if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
We hope we have been able to give you the most important information about data processing by Google Analytics. If you would like to learn more about the tracking service, we recommend these two links: https://marketingplatform.google.com/about/analytics/terms/de/ and https://support.google.com/analytics/answer/6004245?hl=de.
If you would like to learn more about data processing, please refer to the Google privacy policy at https://policies.google.com/privacy?hl=de.
Data Processing Agreement (DPA) Google Analytics
In accordance with Article 28 of the General Data Protection Regulation (GDPR), we have concluded a data processing agreement (DPA) with Google. You can read exactly what a DPA is and, above all, what a DPA must contain in our general section “Data Processing Agreement (DPA)”.
This agreement is required by law because Google processes personal data on our behalf. It clarifies that Google may only process data it receives from us in accordance with our instructions and must comply with the GDPR. You can find the link to the data processing terms at https://business.safety.google/intl/de/adsprocessorterms/
Google Analytics Demographics and Interests Reports
We have enabled the advertising reporting features in Google Analytics. The demographics and interests reports contain information on age, gender and interests. This allows us to gain a better picture of our users – without being able to attribute this data to individual persons. You can learn more about the advertising features at https://support.google.com/analytics/answer/3450482?hl=de_AT&utm_id=ad.
You can stop the use of the activities and information of your Google account under “Ad Settings” at https://adssettings.google.com/authenticated by means of a checkbox.
Google Analytics in Consent Mode
Depending on your consent, your personal data is processed by Google Analytics in what is known as consent mode (“Consent Mode”). You can choose whether or not to consent to Google Analytics cookies. In doing so, you also choose which of your data Google Analytics may process. The data collected is mainly used to measure user behaviour on the website, to deliver targeted advertising and to provide us with web analytics reports. As a rule, you consent to data processing by Google via a cookie consent tool. If you do not consent to data processing, only aggregated data is collected and processed. This means that data cannot be attributed to individual users and therefore no user profile is created about you. You can also consent to statistical measurement only. In this case, no personal data is processed and consequently it is not used for advertising or for measuring advertising success.
Google Analytics IP Anonymisation
We have implemented Google Analytics IP address anonymisation on this website. This feature was developed by Google so that this website can comply with the applicable data protection regulations and the recommendations of local data protection authorities where these prohibit the storage of the full IP address. The anonymisation or masking of the IP takes place as soon as the IP addresses arrive in the Google Analytics data collection network and before any storage or processing of the data takes place.
You can find more information on IP anonymisation at https://support.google.com/analytics/answer/2763052?hl=de.
Contact Form
Our contact and enquiry forms are processed entirely on our own web server — no external form service provider is involved. When you submit a form, the data you have entered (e.g. name, e-mail address, telephone number if applicable, company and your message) is transmitted to us exclusively by e-mail in order to handle and respond to your enquiry. The data is not stored in a database or in log files on the web server and is not passed on to third parties. To protect against automated abuse, your IP address is processed for a maximum of 24 hours exclusively in the form of a non-reversible hash value (rate limiting) and is then automatically deleted. The legal basis for the processing is the implementation of pre-contractual measures at your request (Art. 6(1)(b) GDPR) as well as your consent (Art. 6(1)(a) GDPR), which you give via the checkbox on the form. We only retain enquiries received by e-mail for as long as is necessary to handle your request and to comply with statutory retention obligations.
Google reCAPTCHA Privacy Policy
To protect our forms against spam and automated abuse, we use Google reCAPTCHA (version 3, invisible in the background). The service provider is the American company Google Inc.; for the European region, Google Ireland Limited (Gordon House, Barrow Street, Dublin 4, Ireland) is responsible. The reCAPTCHA service is only loaded when you interact with a form on our website. In doing so, data such as your IP address, browser and device information and your interaction behaviour on the page are transmitted to Google and evaluated there in order to assess whether the input comes from a human or a program. A transfer of data to the USA cannot be ruled out in this context. Google is an active participant in the EU-US Data Privacy Framework and also uses standard contractual clauses (Art. 46(2) and (3) GDPR) as the basis for data transfers to third countries. The legal basis for the use is our legitimate interest (Art. 6(1)(f) GDPR) in protecting our website against spam, abuse and automated attacks. You can find more information on the data processed by reCAPTCHA in Google’s privacy policy at https://policies.google.com/privacy and in the terms of service at https://policies.google.com/terms.
Google Optimize Privacy Policy
We use Google Optimize, a website optimisation tool, on our website. The service provider is the American company Google Inc. For the European region, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
You can learn more about the data processed through the use of Google Optimize in the Privacy Policy at https://policies.google.com/privacy?hl=de.
Data Processing Agreement (DPA) Google Optimize
In accordance with Article 28 of the General Data Protection Regulation (GDPR), we have concluded a data processing agreement (DPA) with Google. You can read exactly what a DPA is and, above all, what a DPA must contain in our general section “Data Processing Agreement (DPA)”.
This agreement is required by law because Google processes personal data on our behalf. It clarifies that Google may only process data it receives from us in accordance with our instructions and must comply with the GDPR. You can find the link to the data processing terms at https://business.safety.google/intl/de/adsprocessorterms/
Google Site Kit Privacy Policy
| Google Site Kit Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: evaluation of visitor information to optimise the web offering. 📓 Data processed: access statistics containing data such as access locations, device data, access duration and time, navigation behaviour, click behaviour and IP addresses. You can find more details on this further below and in the Google Analytics privacy policy. 📅 Storage period: depending on the properties used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Site Kit?
We have integrated the WordPress plugin Google Site Kit of the American company Google Inc. into our website. For the European region, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. With Google Site Kit, we can quickly and easily view statistics originating from various Google products such as Google Analytics directly in our WordPress dashboard. The tool, or rather the tools integrated into Google Site Kit, also collect personal data from you, among other things. In this privacy policy, we explain why we use Google Site Kit, how long and where data is stored and which other privacy texts are relevant to you in this context.
Google Site Kit is a plugin for the content management system WordPress. With this plugin, we can view important website analysis statistics directly in our dashboard. These are statistics collected by other Google products, above all by Google Analytics. In addition to Google Analytics, the services Google Search Console, Page Speed Insight, Google AdSense, Google Optimize and Google Tag Manager can also be linked to Google Site Kit.
Why do we use Google Site Kit on our website?
As a service provider, it is our task to offer you the best possible experience on our website. You should feel comfortable on our website and find exactly what you are looking for quickly and easily. Statistical evaluations help us to get to know you better and to adapt our offering to your wishes and interests. We use various Google tools for these evaluations. Site Kit makes our work much easier in this respect, because we can view and analyse the statistics of the Google products directly in the dashboard. We therefore no longer have to log in separately to each tool. Site Kit thus always provides a good overview of the most important analytics data.
What data is stored by Google Site Kit?
If you have actively consented to tracking tools in the cookie notice (also called script or banner), cookies are set by Google products such as Google Analytics and data about you, for example about your user behaviour, is sent to Google, stored and processed there. This also includes the storage of personal data such as your IP address.
For more detailed information on the individual services, we have separate text sections in this privacy policy. Take a look, for example, at our privacy policy on Google Analytics. There we go into great detail about the data collected. You will learn how long Google Analytics stores, manages and processes data, which cookies may be used and how you can prevent data storage. Likewise, we also have separate privacy policies with comprehensive information for other Google services such as Google Tag Manager or Google AdSense.
Below we show you example Google Analytics cookies that may be set in your browser, provided you have generally consented to data processing by Google. Please note that these cookies are merely a selection:
Name: _ga
Value:2.1326744211.152122821163-2
Purpose: By default, analytics.js uses the _ga cookie to store the user ID. Basically, it serves to distinguish between website visitors.
Expiry date: after 2 years
Name: _gid
Value:2.1687193234.152122821163-7
Purpose: This cookie also serves to distinguish between website visitors.
Expiry date: after 24 hours
Name: _gat_gtag_UA_<property-id>
Value: 1
Purpose: This cookie is used to throttle the request rate.
Expiry date: after 1 minute
How long and where are the data stored?
Google stores collected data on its own Google servers, which are distributed worldwide. Most of the servers are located in the United States, and it is therefore quite possible that your data will also be stored there. At https://www.google.com/about/datacenters/locations/?hl=de you can see exactly where the company provides servers.
Data collected by Google Analytics is retained for 26 months by default. Your user data is then deleted. The retention period applies to all data linked to cookies, user recognition and advertising IDs.
How can I delete my data or prevent data storage?
You always have the right to obtain information about your data and to have your data erased, rectified or restricted. In addition, you can also deactivate, delete or manage cookies in your browser at any time.
If you generally wish to deactivate, delete or manage cookies, you will find the relevant links to the respective instructions for the most popular browsers in the section “Cookies”.
Legal basis
The use of Google Site Kit requires your consent, which we have obtained with our cookie popup. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data, as may occur when data is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offering technically and economically. With the help of Google Site Kit, we detect website errors, can identify attacks and improve economic efficiency. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Site Kit if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
To learn more about data processing by Google, we recommend Google’s comprehensive privacy policy at https://policies.google.com/privacy?hl=de.
Social Media Introduction
| Social Media Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: presentation and optimisation of our services, contact with visitors, prospective customers, etc., advertising 📓 Data processed: data such as telephone numbers, e-mail addresses, contact data, data on user behaviour, information about your device and your IP address. You can find more details on this in the respective social media tool used. 📅 Storage period: depending on the social media platforms used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is social media?
In addition to our website, we are also active on various social media platforms. In this context, user data may be processed so that we can specifically address users who are interested in us via the social networks. Furthermore, elements of a social media platform may also be embedded directly in our website. This is the case, for example, if you click on a so-called social button on our website and are forwarded directly to our social media presence. So-called social media are websites and apps through which registered members can produce content, exchange content openly or in certain groups and network with other members.
Why do we use social media?
For years, social media platforms have been the place where people communicate and get in touch online. With our social media presences, we can bring our products and services closer to interested parties. The social media elements integrated on our website help you to switch to our social media content quickly and without complications.
The data stored and processed through your use of a social media channel is primarily intended to enable web analyses to be carried out. The aim of these analyses is to be able to develop more precise and personalised marketing and advertising strategies. Depending on your behaviour on a social media platform, appropriate conclusions about your interests can be drawn with the help of the evaluated data and so-called user profiles can be created. This also enables the platforms to present you with tailored advertisements. In most cases, cookies are set in your browser for this purpose, which store data about your usage behaviour.
As a rule, we assume that we remain the controller under data protection law even when we use the services of a social media platform. However, the European Court of Justice has ruled that in certain cases the operator of the social media platform may be a joint controller together with us within the meaning of Art. 26 GDPR. Where this is the case, we will point this out separately and work on the basis of a corresponding agreement. The essence of the agreement is then set out further below for the platform concerned.
Please note that when using the social media platforms or our integrated elements, your data may also be processed outside the European Union, as many social media channels, for example Facebook or Twitter, are American companies. As a result, you may no longer be able to claim or enforce your rights with regard to your personal data as easily.
What data is processed?
Exactly which data is stored and processed depends on the respective provider of the social media platform. Usually, however, it is data such as telephone numbers, e-mail addresses, data that you enter in a contact form, user data such as which buttons you click, whom you like or follow, when you visited which pages, information about your device and your IP address. Most of this data is stored in cookies. Especially if you yourself have a profile on the social media channel visited and are logged in, data may be linked to your profile.
All data collected via a social media platform is also stored on the providers’ servers. Consequently, only the providers have access to the data and can provide you with the relevant information or make changes.
If you want to know exactly which data is stored and processed by the social media providers and how you can object to the data processing, you should carefully read the respective privacy policy of the company. Also, if you have questions about data storage and data processing or wish to assert corresponding rights, we recommend that you contact the provider directly.
Duration of data processing
We will inform you about the duration of the data processing further below, provided we have further information on this. For example, the social media platform Facebook stores data until it is no longer needed for its own purposes. Customer data that is matched with its own user data, however, is deleted within two days. In general, we only process personal data for as long as is absolutely necessary for the provision of our services and products. Where required by law, for example in the case of accounting, this storage period may also be exceeded.
Right to object
You also have the right and the option to withdraw your consent to the use of cookies or third-party providers such as embedded social media elements at any time. This works either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting the cookies in your browser.
As cookies may be used by social media tools, we also recommend our general privacy policy on cookies. To find out exactly which of your data is stored and processed, you should read the privacy policies of the respective tools.
Legal basis
If you have consented to your data being processed and stored by integrated social media elements, this consent constitutes the legal basis for the data processing (Art. 6(1)(a) GDPR). In principle, where consent has been given, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and good communication with you or other customers and business partners. Nevertheless, we only use the tools if you have given your consent. Most social media platforms also set cookies in your browser to store data. We therefore recommend that you read our privacy text on cookies carefully and look at the privacy policy or cookie policy of the respective service provider.
Information on specific social media platforms – where available – can be found in the following sections.
Facebook Privacy Policy
| Facebook Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our services 📓 Data processed: data such as customer data, data on user behaviour, information about your device and your IP address. You can find more details on this further below in the privacy policy. 📅 Storage period: until the data is no longer useful for Facebook’s purposes ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are Facebook tools?
We use selected Facebook tools on our website. Facebook is a social media network of the company Meta Platforms Inc. or, for the European region, of the company Meta Platforms Ireland Limited, 4 Grand Canal Square, Grand Canal Harbour, Dublin 2, Ireland. With the help of these tools, we can offer you and people who are interested in our products and services the best possible offering.
If data about you is collected and forwarded via our embedded Facebook elements or via our Facebook page (fan page), both we and Facebook Ireland Ltd. are responsible for this. Facebook alone is responsible for the further processing of this data. Our joint obligations have also been laid down in a publicly accessible agreement at https://www.facebook.com/legal/controller_addendum. It states, for example, that we must clearly inform you about the use of Facebook tools on our site. Furthermore, we are also responsible for ensuring that the tools are integrated into our website in a manner that is secure under data protection law. Facebook, on the other hand, is responsible, for example, for the data security of the Facebook products. If you have any questions about data collection and data processing by Facebook, you can contact the company directly. If you address the question to us, we are obliged to forward it to Facebook.
Below we provide an overview of the various Facebook tools, which data is sent to Facebook and how you can delete this data.
In addition to many other products, Facebook also offers the so-called “Facebook Business Tools”. This is Facebook’s official name. However, as the term is hardly known, we have decided to simply call them Facebook tools. These include, among others:
- Facebook Pixel
- social plug-ins (such as the “Like” or “Share” button)
- Facebook Login
- Account Kit
- APIs (application programming interfaces)
- SDKs (collections of programming tools)
- Platform integrations
- Plugins
- Codes
- Specifications
- Documentation
- Technologies and services
Through these tools, Facebook extends its services and has the opportunity to obtain information about user activities outside of Facebook.
Why do we use Facebook tools on our website?
We only want to show our services and products to people who are genuinely interested in them. With the help of advertisements (Facebook Ads), we can reach exactly these people. However, in order for suitable advertising to be shown to users, Facebook needs information about people’s wishes and needs. Information about user behaviour (and contact data) on our website is therefore made available to the company. As a result, Facebook collects better user data and can display suitable advertising for our products or services to interested people. The tools thus enable tailored advertising campaigns on Facebook.
Facebook calls data about your behaviour on our website “event data”. This is also used for measurement and analysis services. Facebook can thus create “campaign reports” on our behalf about the effectiveness of our advertising campaigns. Furthermore, analyses give us better insight into how you use our services, website or products. As a result, we use some of these tools to optimise your user experience on our website. For example, with the social plug-ins you can share content from our site directly on Facebook.
What data is stored by Facebook tools?
Through the use of individual Facebook tools, personal data (customer data) may be sent to Facebook. Depending on the tools used, customer data such as name, address, telephone number and IP address may be transmitted.
Facebook uses this information to match the data with the data it holds about you itself (provided you are a Facebook member). Before customer data is transmitted to Facebook, so-called “hashing” takes place. This means that a data set of any size is transformed into a character string. This also serves to encrypt data.
In addition to the contact data, “event data” is also transmitted. “Event data” refers to the information we receive about you on our website. For example, which subpages you visit or which products you buy from us. Facebook does not share the information it receives with third parties (such as advertisers) unless the company has explicit permission or is legally obliged to do so. “Event data” can also be linked to contact data. This allows Facebook to offer better personalised advertising. After the matching process already mentioned, Facebook deletes the contact data again.
In order to deliver advertisements in an optimised manner, Facebook only uses the event data once it has been combined with other data (collected by Facebook in other ways). Facebook also uses this event data for security, protection, development and research purposes. Much of this data is transferred to Facebook via cookies. Cookies are small text files used to store data or information in browsers. Depending on the tools used and on whether you are a Facebook member, a varying number of cookies are created in your browser. In the descriptions of the individual Facebook tools, we go into more detail on individual Facebook cookies. You can also find general information on the use of Facebook cookies at https://www.facebook.com/policies/cookies.
How long and where are the data stored?
In principle, Facebook stores data until it is no longer needed for its own services and Facebook products. Facebook has servers distributed all over the world where its data is stored. Customer data, however, is deleted within 48 hours after it has been matched against Facebook's own user data.
How can I delete my data or prevent data storage?
In accordance with the General Data Protection Regulation, you have the right to access, rectification, portability and erasure of your data.
Complete deletion of the data only takes place if you delete your Facebook account entirely. This is how deleting your Facebook account works:
1) On the right-hand side of Facebook, click on Settings.
2) Then click on „Your Facebook Information“ in the left-hand column.
3) Now click on “Deactivation and Deletion”.
4) Now select „Delete account“ and then click on „Continue to account deletion“
5) Now enter your password, click on „Continue“ and then on „Delete account“
The data that Facebook receives via our website is stored, among other things, by means of cookies (e.g. in the case of social plugins). In your browser, you can deactivate, delete or manage individual cookies or all cookies. This works differently depending on which browser you use. In the „Cookies“ section you will find the relevant links to the respective instructions for the most popular browsers.
If you generally do not want any cookies, you can set up your browser so that it always informs you when a cookie is about to be set. This allows you to decide for each individual cookie whether to allow it or not.
Legal basis
If you have consented to your data being processed and stored by integrated Facebook tools, this consent constitutes the legal basis for the data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and effective communication with you or other customers and business partners. Nevertheless, we only use the tools insofar as you have given your consent. Most social media platforms also set cookies in your browser to store data. We therefore recommend that you read our privacy text on cookies carefully and consult the privacy policy or cookie policy of Facebook.
Facebook also processes your data in the USA, among other places. Facebook or Meta Platforms is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Facebook uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Facebook undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Facebook data processing terms, which refer to the standard contractual clauses, at https://www.facebook.com/legal/terms/dataprocessing.
We hope we have given you the most important information about the use of and data processing by the Facebook tools. If you would like to find out more about how Facebook uses your data, we recommend the data policy at https://www.facebook.com/privacy/policy/.
Facebook Login Privacy Policy
We have integrated the convenient Facebook Login on our website. This allows you to log in to our site easily with your Facebook account, without having to create an additional user account. If you decide to register via Facebook Login, you will be redirected to the social media network Facebook. There, you log in using your Facebook user data. Through this login procedure, data about you and your user behaviour is stored and transmitted to Facebook.
Facebook uses various cookies to store the data. Below we show you the most important cookies that are set in your browser, or already exist, when you log in to our website via Facebook Login:
Name: fr
Value: 0jieyh4c2GnlufEJ9..Bde09j…1.0.Bde09j
Purpose: This cookie is used to ensure that the social plugin on our website works as well as possible.
Expiry date: after 3 months
Name: datr
Value: 4Jh7XUA2122821163SEmPsSfzCOO4JFFl
Purpose: Facebook sets the “datr” cookie when a web browser accesses facebook.com, and the cookie helps to identify login activities and to protect users.
Expiry date: after 2 years
Name: _js_datr
Value: deleted
Purpose: Facebook sets this session cookie for tracking purposes, even if you do not have a Facebook account or are logged out.
Expiry date: after end of session
Note: The cookies listed are only a small selection of the cookies available to Facebook. Other cookies include, for example, _ fbp, sb or wd. A complete list is not possible, as Facebook has a large number of cookies at its disposal and uses them variably.
On the one hand, Facebook Login offers you a quick and easy registration process; on the other hand, it gives us the opportunity to share data with Facebook. This enables us to better tailor our offering and our promotional campaigns to your interests and needs. The data we receive from Facebook in this way is public data such as
- Your Facebook name
- Your profile picture
- a stored e-mail address
- Friends lists
- Button information (e.g. „Like“ button)
- Date of birth
- Language
- Place of residence
In return, we provide Facebook with information about your activities on our website. This includes, among other things, information about the device you use, which subpages of our site you visit or which products you have purchased from us.
By using Facebook Login, you consent to the data processing. You can revoke this agreement at any time. If you would like more information about data processing by Facebook, we recommend the Facebook privacy policy at https://www.facebook.com/privacy/policy/.
If you are logged in to Facebook, you can change your settings for advertisements yourself at https://www.facebook.com/adpreferences/advertisers/?entry_product=ad_settings_screen.
Facebook Social Plug-ins Privacy Policy
So-called social plug-ins of the company Meta Platforms Inc. are integrated on our website. You can recognise these buttons by the classic Facebook logo, such as the „Like“ button (the hand with a raised thumb), or by a clear „Facebook Plug-in“ label. A social plug-in is a small part of Facebook that is integrated into our website. Each plug-in has its own function. The most frequently used functions are the well-known “Like” and “Share” buttons.
The following social plug-ins are offered by Facebook:
- “Save” button
- “Like” button, Share, Send and Quote
- Page plug-in
- Comments
- Messenger plug-in
- Embedded posts and video player
- Groups plug-in
At https://developers.facebook.com/docs/plugins you can obtain more detailed information on how the individual plug-ins are used. We use the social plug-ins on the one hand to offer you a better user experience on our website and on the other hand because Facebook can use them to optimise our advertisements.
If you have a Facebook account or have ever visited https://www.facebook.com/, Facebook has already set at least one cookie in your browser. In this case, your browser sends information to Facebook via this cookie as soon as you visit our website or interact with social plug-ins (e.g. the „Like“ button).
The information received is deleted or anonymised within 90 days. According to Facebook, this data includes your IP address, which website you visited, the date, the time and other information relating to your browser.
To prevent Facebook from collecting a large amount of data during your visit to our website and linking it with the Facebook data, you must log out of Facebook during your visit to the website.
If you are not logged in to Facebook or do not have a Facebook account, your browser sends less information to Facebook because you have fewer Facebook cookies. Nevertheless, data such as your IP address or which website you visit may be transmitted to Facebook. We would like to point out explicitly that we do not know the exact content of the data. However, we try to inform you about the data processing as well as possible according to our current state of knowledge. You can also read how Facebook uses the data in the company's data policy at https://www.facebook.com/about/privacy/update.
At least the following cookies are set in your browser when you visit a website with Facebook social plug-ins:
Name: dpr
Value: not specified
Purpose: This cookie is used so that the social plug-ins on our website work.
Expiry date: after end of session
Name: fr
Value: 0jieyh4122821163c2GnlufEJ9..Bde09j…1.0.Bde09j
Purpose: This cookie is also necessary for the plug-ins to function properly.
Expiry date:: after 3 months
Note: These cookies were set after a test, even if you are not a Facebook member.
If you are logged in to Facebook, you can change your settings for advertisements yourself at https://www.facebook.com/adpreferences/advertisers/. If you are not a Facebook user, you can generally manage your usage-based online advertising at https://www.youronlinechoices.com/de/praferenzmanagement/?tid=122821163. There you have the option of deactivating or activating providers.
If you would like to find out more about Facebook's data protection, we recommend the company's own data policy at https://www.facebook.com/privacy/policy/.
Instagram Privacy Policy
| Instagram Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Optimisation of our service 📓 Processed data: Data such as data on user behaviour, information about your device and your IP address. You can find more details on this further below in this privacy policy. 📅 Storage period: until Instagram no longer needs the data for its purposes ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Instagram?
We have integrated functions of Instagram on our website. Instagram is a social media platform of the company Instagram LLC, 1601 Willow Rd, Menlo Park CA 94025, USA. Since 2012, Instagram has been a subsidiary of Meta Platforms Inc. and is one of the Facebook products. Integrating Instagram content on our website is called embedding. This allows us to show you content such as buttons, photos or videos from Instagram directly on our website. When you access web pages of our web presence that have an integrated Instagram function, data is transmitted to, stored and processed by Instagram. Instagram uses the same systems and technologies as Facebook. Your data is therefore processed across all Facebook companies.
In the following, we want to give you a more detailed insight into why Instagram collects data, what data is involved and how you can largely control the data processing. As Instagram belongs to Meta Platforms Inc., we obtain our information on the one hand from the Instagram policies, but on the other hand also from the Meta privacy policies themselves.
Instagram is one of the best-known social media networks worldwide. Instagram combines the advantages of a blog with the advantages of audiovisual platforms such as YouTube or Vimeo. On „Insta“ (as many users casually call the platform) you can upload photos and short videos, edit them with various filters and also share them on other social networks. And if you do not want to be active yourself, you can also just follow other interesting users.
Why do we use Instagram on our website?
Instagram is the social media platform that has really taken off in recent years. And of course we have also responded to this boom. We want you to feel as comfortable as possible on our website. That is why a varied presentation of our content is a matter of course for us. Through the embedded Instagram functions, we can enrich our content with helpful, funny or exciting content from the world of Instagram. Since Instagram is a subsidiary of Facebook, the data collected can also be useful to us for personalised advertising on Facebook. In this way, our advertisements are only shown to people who are genuinely interested in our products or services.
Instagram also uses the collected data for measurement and analysis purposes. We receive aggregated statistics and thus more insight into your wishes and interests. It is important to mention that these reports do not identify you personally.
What data is stored by Instagram?
When you come across one of our pages that has Instagram functions (such as Instagram images or plug-ins) integrated, your browser automatically connects to Instagram's servers. In the process, data is sent to, stored and processed by Instagram. This happens regardless of whether you have an Instagram account or not. This includes information about our website, about your computer, about purchases made, about advertisements you see and how you use our offering. Furthermore, the date and time of your interaction with Instagram are also stored. If you have an Instagram account or are logged in, Instagram stores significantly more data about you.
Facebook distinguishes between customer data and event data. We assume that this is exactly the case with Instagram as well. Customer data includes, for example, name, address, telephone number and IP address. This customer data is only transmitted to Instagram once it has first been „hashed“. Hashing means that a data record is converted into a character string. This makes it possible to encrypt the contact data. In addition, the „event data“ mentioned above is also transmitted. By „event data“, Facebook – and consequently Instagram – means data about your user behaviour. It may also happen that contact data is combined with event data. The collected contact data is matched against the data that Instagram already holds about you.
The collected data is transmitted to Facebook via small text files (cookies), which are usually set in your browser. Depending on the Instagram functions used and whether you have an Instagram account yourself, varying amounts of data are stored.
We assume that data processing at Instagram works in the same way as at Facebook. This means: if you have an Instagram account or have visited www.instagram.com, Instagram has set at least one cookie. If this is the case, your browser sends information to Instagram via the cookie as soon as you come into contact with an Instagram function. This data is deleted or anonymised again after 90 days (after matching) at the latest. Although we have studied Instagram's data processing in depth, we cannot say exactly what data Instagram collects and stores.
Below we show you cookies that are set in your browser at a minimum when you click on an Instagram function (such as a button or an Insta image). In our test, we assume that you do not have an Instagram account. If you are logged in to Instagram, significantly more cookies are of course set in your browser.
These cookies were used in our test:
Name: csrftoken
Value: “”
Purpose: This cookie is most likely set for security reasons to prevent request forgery. However, we were unable to find out more precise details.
Expiry date: after one year
Name: mid
Value: “”
Purpose: Instagram sets this cookie to optimise its own services and offerings on and off Instagram. The cookie assigns a unique user ID.
Expiry date: after end of session
Name: fbsr_122821163124024
Value: not specified
Purpose: This cookie stores the login request for users of the Instagram app.
Expiry date: after end of session
Name: rur
Value: ATN
Purpose: This is an Instagram cookie that ensures functionality on Instagram.
Expiry date: after end of session
Name: urlgen
Value: “{”194.96.75.33”: 1901}:1iEtYv:Y833k2_UjKvXgYe122821163”
Purpose: This cookie serves Instagram's marketing purposes.
Expiry date: after end of session
Note: We cannot claim completeness here. Which cookies are set in an individual case depends on the embedded functions and your use of Instagram.
How long and where are the data stored?
Instagram shares the information it receives among the Facebook companies, with external partners and with people you connect with worldwide. Data processing is carried out in compliance with its own data policy. Your data is distributed across Facebook servers all over the world, among other things for security reasons. Most of these servers are located in the USA.
How can I delete my data or prevent data storage?
Thanks to the General Data Protection Regulation, you have the right to access, portability, rectification and erasure of your data. You can manage your data in the Instagram settings. If you want to delete your data on Instagram completely, you must delete your Instagram account permanently.
And this is how deleting your Instagram account works:
First open the Instagram app. On your profile page, scroll down and click on „Help Centre“. You will now be taken to the company's website. On the website, click on „Managing Your Account“ and then on „Delete Your Account“.
If you delete your account completely, Instagram deletes posts such as your photos and status updates. Information that other people have shared about you does not belong to your account and is therefore not deleted.
As already mentioned above, Instagram stores your data primarily via cookies. You can manage, deactivate or delete these cookies in your browser. Depending on your browser, management always works slightly differently. In the „Cookies“ section you will find the relevant links to the respective instructions for the most popular browsers.
You can also generally set up your browser so that you are always informed when a cookie is about to be set. You can then always decide individually whether you want to allow the cookie or not.
Legal basis
If you have consented to your data being processed and stored by integrated social media elements, this consent constitutes the legal basis for the data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and effective communication with you or other customers and business partners. Nevertheless, we only use the integrated social media elements insofar as you have given your consent. Most social media platforms also set cookies in your browser to store data. We therefore recommend that you read our privacy text on cookies carefully and consult the privacy policy or cookie policy of the respective service provider.
Instagram also processes your data in the USA, among other places. Instagram or Meta Platforms is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Instagram uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Instagram undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
We have tried to give you the most important information about data processing by Instagram. At https://privacycenter.instagram.com/policy/ you can familiarise yourself further with Instagram's data policies.
Snapchat Privacy Policy
| Snapchat Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Optimisation of our service 📓 Processed data: Data such as data on user behaviour, information about your device and your IP address. You can find more details on this further below in this privacy policy. 📅 Storage period: depends on the type of data ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Snapchat?
For our website, we also use integrations of the messaging and social media service Snapchat. The service provider is the American company Snap Inc., 2772 Donald Douglas Loop N, Santa Monica (HQ), CA, USA.
With Snapchat, users can create so-called „Snaps“, i.e. short images or videos, and share them with friends or followers. Snapchat is a popular communication tool, especially among younger people. Unlike with other social media tools, these „Snaps“ are deleted again after a limited period of time. Depending on the user's preferences, this time can be set from a few seconds up to 24 hours. In addition, Snapchat also offers functions such as group chats, video calls and a Discover section for media companies.
Why do we use Snapchat on our website?
We have provided Snapchat functions on our website so that we can also draw attention to Snapchat content and so that you also have the opportunity to follow us on Snapchat. This allows us to stay in contact with you beyond our website presence as well. By integrating Snapchat content, we also offer all our visitors who are not on Snapchat the opportunity to gain an insight into the world of Snapchat. We therefore regard the integration as part of our overall offering on our website.
What data is processed by Snapchat?
When you view or interact with Snapchat content via our website, Snapchat may collect information about your usage behaviour and your device. This may include data such as your IP address, browser type, operating system, location, language settings and other technical information. Snapchat may also use cookies and similar technologies to collect information and personalise your user experience.
If you have or create a Snapchat account yourself, further information may also be collected and processed. In this case, you voluntarily disclose data such as your name, user name, e-mail address, telephone number and date of birth. If you make a purchase within the app, you must also provide payment data. All of this information is processed by Snapchat, provided you make this data available. If you actively use the service with your account, all information sent via Snapchat is also processed. This information includes, for example, chats, conversations, images and videos.
How long and where are the data stored?
Snapchat stores different data for different lengths of time, and the Snapchat servers are distributed across various regions worldwide. This means that your data may also be processed in the USA, for example. As already mentioned above, the storage period of „Snaps“ can partly be chosen by yourself in the settings. Most messages sent in the tool are automatically deleted from the servers as soon as they have been received or have expired. However, there is also data that is stored for significantly longer. This includes account information such as name, mobile phone number or e-mail address. The storage period of location data depends on how precise it is and which of the Snapchat services is used.
At https://help.snapchat.com/hc/de/articles/7012334940948 you will find a fairly good overview of the storage periods of various Snapchat data.
How can I delete my data or prevent data storage?
If you have a Snapchat account, you can manage your privacy settings directly on Snapchat and determine the storage period of various content yourself. For example, in the settings of your Snapchat account you can specify whether “Snaps” are deleted after a few seconds or only after 24 hours. In addition, you can also directly ask those responsible at Snapchat to delete your personal data. However, the Snapchat privacy policy points out that, although most data is deleted, for legal reasons it may be the case that data deletion has to be suspended or that some data remains stored.
In addition, you can manage and deactivate cookies that Snapchat may set in your web browser in order to limit data collection. This is also possible without a Snapchat account. Please note, however, that this may impair the functionality of our website.
Legal basis
If you have consented to your data being processed and stored by Snapchat, this consent constitutes the legal basis for the data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and good communication with you or other customers and business partners. Nevertheless, we only use the integrated Snapchat elements insofar as you have given your consent. Snapchat may also set cookies in your browser to store data. We therefore recommend that you read our privacy policy text on cookies carefully and review the privacy policy or cookie policies of the respective service provider.
Snap also processes your data in the USA, among other places. We would like to point out that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the USA. This may entail various risks for the lawfulness and security of data processing.
As the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, Norway, and thus in particular in the USA) or for data transfers to such recipients, Snap uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through these clauses, Snap undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses, among other places, here: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find more information on the standard contractual clauses at Snap at https://snap.com/en-US/terms/standard-contractual-clauses.
You can find out more about the data processed through the use of Snapchat in the privacy policy at https://snap.com/de-DE/privacy/privacy-policy.
TikTok Privacy Policy
| TikTok Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service 📓 Processed data: for example, your IP address, browser data, and the date and time of your page view may be stored You can find more details on this further below in this privacy policy. 📅 Storage period: varies depending on settings ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is TikTok?
We use the TikTok integration on our website. The service provider is the Chinese company Beijing Bytedance Technology Ltd. For the European region, the Irish company TikTok Technology Limited, 10 Earlsfort Terrace, Dublin, D02 T380, Ireland, is responsible. TikTok is a social media platform that is particularly popular among young people, on which users can create, share and watch short video clips.
In this privacy policy, we inform you about which data is processed by TikTok, how long the data is stored and how you can manage your privacy settings.
Why do we use TikTok on our website?
We have integrated TikTok into our website so that you can watch TikTok videos if you feel like it and, where applicable, interact with the videos. TikTok is particularly known for funny and creative content, and of course we do not want to withhold such content from you. After all, we ourselves also enjoy watching the odd creative TikTok video.
What data is processed by TikTok?
If you watch or interact with TikTok videos on our website, TikTok may collect information about your usage behaviour and your device. This may include data such as your IP address, browser type, operating system, location and other technical information. TikTok may also use cookies and similar technologies to collect information and personalise your user experience.
If you have a TikTok account yourself, further information may also be collected and processed. This includes, for example, user information (such as name, date of birth or your e-mail address) and data about your communication with other TikTok users.
How long and where are the data stored?
The storage period and storage locations of the data collected by TikTok can vary considerably and are subject to TikTok’s privacy policies. TikTok may also store data on servers in the USA and other countries. The storage period is generally based on the respective legal requirements and internal policies. However, we have not yet been able to find out exactly how long data is stored. As soon as we have more detailed information, we will of course inform you accordingly.
How can I delete my data or prevent data storage?
If you have a TikTok account, you can manage your privacy settings directly on TikTok. For example, in the settings of your TikTok account you can specify which information may be shared and which may not. In addition, you can manage and deactivate cookies in your web browser in order to limit data collection. This is of course also possible without a TikTok account. Please note, however, that this may affect the functionality of our website and your TikTok experience.
Legal basis
If you have consented to your data being processed and stored by TikTok, this consent constitutes the legal basis for the data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and good communication with you or other customers and business partners. Nevertheless, we only use the integrated social media elements insofar as you have given your consent. TikTok may also set cookies in your browser to store data. We therefore recommend that you read our privacy policy text on cookies carefully and review the privacy policy or cookie policies of the respective service provider.
TikTok also processes your data in the USA, among other places. We would like to point out that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the USA. This may entail various risks for the lawfulness and security of data processing.
As the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, Norway, and thus in particular in the USA) or for data transfers to such recipients, TikTok uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through these clauses, TikTok undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses, among other places, here: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find further information on TikTok’s privacy policy and on the collection of data by TikTok on the TikTok website at https://www.tiktok.com/legal/page/eea/privacy-policy/en and in the general information about TikTok at https://www.tiktok.com/en/.
X (formerly Twitter) Privacy Policy
| X (formerly Twitter) Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service 📓 Processed data: data such as data on user behaviour, information about your device and your IP address. You can find more details on this further below in this privacy policy. 📅 Storage period: X deletes data collected from other websites after 30 days at the latest ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is X?
We have integrated functions of X into our website. These include, for example, embedded tweets, timelines, buttons or hashtags. X is a short message service and social media platform of the American company X Corp., 1355 Market Street, Suite 900 San Francisco, CA 94103, USA. For the European region, the company Twitter International Unlimited Company (One Cumberland Place, Fenian Street, Dublin 2, D02 AX07, Ireland) is responsible for the processing of personal data.
To our knowledge, in the European Economic Area and in Switzerland, the mere integration of X functions does not yet transfer any personal data or data about your web activities to X. Only when you interact with the X functions, for example by clicking a button, can data be sent to X and stored and processed there. We have no influence on this data processing and bear no responsibility for it. In this privacy policy, we want to give you an overview of what data X stores, what X does with this data and how you can largely protect yourself against the data transfer.
For some, X is a news service, for others a social media platform, and still others speak of a microblogging service. All of these designations are justified and mean more or less the same thing.
Both private individuals and companies use X to communicate with interested people via short messages. X allows only 280 characters per message. These messages are called “tweets”. Unlike Facebook, for example, the service does not focus on building a network of “friends”, but wants to be understood as a global and open news platform. On X, you can also have an anonymous account, and tweets can be deleted both by the company and by the users themselves.
Why do we use X on our website?
Like many other websites and companies, we try to offer our services through various channels and to communicate with our customers. X in particular (probably still better known to many as Twitter) has become close to our hearts as a useful “small” news service. Time and again, we tweet or retweet exciting, funny or interesting content. We realise that you cannot follow every channel separately. After all, you have other things to do as well. That is why we have also integrated X functions on our website. You can experience our X activity “on site” or reach our X page via a direct link. Through this integration, we want to strengthen our service and the user-friendliness of our website.
What data is stored by X?
You will find the integrated X functions on some of our subpages. If you interact with the X content, for example by clicking a button, X may collect and store data. This applies even if you do not have an X account yourself. X calls this data “log data”. This includes demographic data, browser cookie IDs, the ID of your smartphone, hashed e-mail addresses, and information about which pages you have visited on X and which actions you have performed. X naturally stores more data if you have an X account and are logged in. Until now, this storage has taken place via cookies. Cookies are small text files that are usually set in your browser and transmit various information to X.
We will now show you which cookies are set if you are not logged in to X but visit a website with integrated X functions. Please regard this list as an example. We can by no means guarantee completeness here, as the choice of cookies is constantly changing and depends on your individual actions with the X content.
These cookies were used in our test:
Name: personalization_id
Value: “v1_cSJIsogU51SeE122821163”
Purpose: This cookie stores information about how you use the website and which advertising may have led you to X.
Expiry date: after 2 years
Name: lang
Value: de
Purpose: This cookie stores your default or preferred language.
Expiry date: after end of session
Name: guest_id
Value: 122821163v1%3A157132626
Purpose: This cookie is set to identify you as a guest.
Expiry date: after 2 years
Name: fm
Value: 0
Purpose: Unfortunately, we were unable to find out the purpose of this cookie.
Expiry date: after end of session
Name: external_referer
Value: 1228211632beTA0sf5lkMrlGt
Purpose: This cookie collects anonymous data, such as how often you visit X and how long you stay on X.
Expiry date: After 6 days
Name: eu_cn
Value: 1
Purpose: This cookie stores user activity and serves various advertising purposes of X.
Expiry date: After one year
Name: ct0
Value: c1179f07163a365d2ed7aad84c99d966
Purpose: Unfortunately, we have not found any information on this cookie.
Expiry date: after 6 hours
Name: _twitter_sess
Value: 53D%253D–dd0248122821163-
Purpose: This cookie enables you to use functions within the X website.
Expiry date: after end of session
Note: X also works with third-party providers. That is why we also detected the three Google Analytics cookies _ga, _gat, _gid during our test.
X uses the collected data on the one hand to better understand user behaviour and thus to improve its own services and advertising offers; on the other hand, the data also serves internal security measures.
How long and where are the data stored?
If X collects data from other websites, this data is deleted, aggregated or otherwise obscured after a maximum of 30 days. The X servers are located in various server centres in the United States. It can therefore be assumed that the collected data is gathered and stored in America. Based on our research, we were unable to determine clearly whether X also has its own servers in Europe. In principle, X may store the collected data until it is no longer useful to the company, until you delete the data or until a statutory deletion period applies.
How can I delete my data or prevent data storage?
X repeatedly emphasises in its privacy policies that it does not store any data from external website visits if you or your browser are located in the European Economic Area or in Switzerland. However, if you interact with X directly, X will of course also store data about you.
If you have an X account, you can manage your data by clicking on “More” under the “Profile” button. Then click on “Settings and privacy”. Here you can manage the data processing individually.
If you do not have an X account, you can go to twitter.com and then click on “Personalisation”. Under the item “Personalisation and data”, you can manage the data collected about you.
As already mentioned above, most data is stored via cookies, and you can manage, deactivate or delete these in your browser. Please note that you only “edit” the cookies in the browser you have chosen. This means: if you use a different browser in the future, you will have to manage your cookies there again according to your wishes. In the “Cookies” section, you will find the corresponding links to the respective instructions for the best-known browsers.
You can also configure your browser so that you are informed about every single cookie. You can then always decide individually whether or not to allow a cookie.
X also uses the data for personalised advertising on and off X. In the settings, you can switch off personalised advertising under “Personalisation and data”. If you use X in a browser, you can deactivate personalised advertising at https://optout.aboutads.info/?c=2&lang=EN.
Legal basis
If you have consented to your data being processed and stored by integrated social media elements, this consent constitutes the legal basis for the data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and effective communication with you or other customers and business partners. Nevertheless, we only use the integrated social media elements insofar as you have given your consent. Most social media platforms also set cookies in your browser to store data. We therefore recommend that you read our privacy text on cookies carefully and consult the privacy policy or cookie policy of the respective service provider.
X also processes your data in the USA, among other places. We would like to point out that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the USA. This may entail various risks for the lawfulness and security of data processing.
As the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, Norway, and thus in particular in the USA) or for data transfers to such recipients, X uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through these clauses, X undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses, among other places, here: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find more information on the standard contractual clauses at X at https://gdpr.twitter.com/en/controller-to-controller-transfers.html.
We hope we have given you a basic overview of the data processing by X. We do not receive any data from X and bear no responsibility for what X does with your data. If you have any further questions on this topic, we recommend the X privacy policy at https://twitter.com/de/privacy.
Content Delivery Networks Introduction
| Content Delivery Networks Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service (so that the website loads faster) 📓 Processed data: data such as your IP address You can find more details on this further below and in the individual privacy policy texts. 📅 Storage period: in most cases, the data is stored until it is no longer required for the provision of the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is a Content Delivery Network?
We use a so-called Content Delivery Network on our website. Such a network is usually just called a CDN. A CDN helps us to load our website quickly and smoothly, regardless of your location. In the process, personal data about you is also stored, managed and processed on the servers of the CDN provider used. Below, we describe the service and its data processing in more detail in general terms. You can find precise information about the handling of your data in the respective privacy policy of the provider.
Every Content Delivery Network (CDN) is a network of regionally distributed servers that are all connected to one another via the internet. Via this network, website content (in particular also very large files) can be delivered quickly and smoothly even during large load peaks. For this purpose, the CDN creates a copy of our website on its servers. Since these servers are distributed worldwide, the website can be delivered quickly. The data transmission to your browser is consequently significantly shortened by the CDN.
Why do we use a Content Delivery Network for our website?
A fast-loading website is part of our service. We of course know how annoying it is when a website loads at a snail’s pace. Most of the time, people even lose patience and leave before the website has fully loaded. Naturally, we want to avoid that. A fast-loading website is therefore a matter of course in our website offering. With a Content Delivery Network, our website loads significantly faster in your browser. The use of the CDN is particularly helpful when you are abroad, because the website is delivered from a server near you.
What data is processed?
When you request a website or the content of a website and this content is cached in a CDN, the CDN forwards the request to the server closest to you, and this server delivers the content. Content Delivery Networks are structured in such a way that JavaScript libraries can be downloaded and are hosted on npm and GitHub servers. Alternatively, with most CDNs, WordPress plugins can also be loaded if they are hosted on WordPress.org. Your browser may send personal data to the Content Delivery Network we use. This includes data such as IP address, browser type, browser version, which web page is loaded, or the time and date of the page visit. This data is collected and also stored by the CDN. Whether cookies are used for data storage depends on the network used. Please read the privacy policy texts of the respective service for this.
Right to object
If you want to prevent this data transfer completely, you can install a JavaScript blocker (see, for example, https://noscript.net/) on your PC. Of course, our website will then no longer be able to offer the usual service (such as a fast loading speed).
Legal basis
If you have consented to the use of a Content Delivery Network, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when data is collected by a Content Delivery Network.
We also have a legitimate interest in using a Content Delivery Network in order to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool insofar as you have given your consent.
Information on specific Content Delivery Networks – where available – can be found in the following sections.
Cloudflare Privacy Policy
| Cloudflare Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service (so that the website loads faster) 📓 Processed data: data such as IP address, contact and log information, security fingerprints and performance data for websites You can find more details on this further below in this privacy policy. 📅 Storage period: in most cases, the data is stored for less than 24 hours ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Cloudflare?
On this website, we use Cloudflare from the company Cloudflare, Inc. (101 Townsend St., San Francisco, CA 94107, USA) to make our website faster and more secure. In doing so, Cloudflare uses cookies and processes user data. Cloudflare, Inc. is an American company that offers a Content Delivery Network and various security services. These services are located between the user and our hosting provider. We will try to explain in more detail below what all of this means exactly.
A Content Delivery Network (CDN), such as the one provided by Cloudflare, is nothing more than a network of connected servers. Cloudflare has distributed such servers all over the world in order to bring websites to your screen faster. Put very simply, Cloudflare creates copies of our website and places them on its own servers. When you now visit our website, a load-balancing system ensures that the largest parts of our website are delivered by the server that can display our website to you the fastest. The data transmission route to your browser is significantly shortened by a CDN. As a result, the content of our website is delivered to you by Cloudflare not only from our hosting server, but from servers all over the world. The use of Cloudflare is particularly helpful for users from abroad, as the page can be delivered from a server nearby. In addition to the fast delivery of websites, Cloudflare also offers various security services, such as DDoS protection or the Web Application Firewall.
Why do we use Cloudflare on our website?
Of course, we want to offer you the best possible service with our website. Cloudflare helps us to make our website faster and more secure. Cloudflare offers us both web optimisations and security services, such as DDoS protection and a web firewall. These also include a reverse proxy and the content distribution network (CDN). Cloudflare blocks threats and limits abusive bots and crawlers that waste our bandwidth and server resources. By storing our website in local data centres and blocking spam software, Cloudflare enables us to reduce our bandwidth usage by around 60%. Providing content via a data centre near you and some web optimisations carried out there reduce the average loading time of a website by around half. According to Cloudflare, the “I´m Under Attack Mode” setting can mitigate further attacks by displaying a JavaScript computing task that must be solved before a user can access a website. Overall, this makes our website significantly more powerful and less susceptible to spam or other attacks.
What data is processed by Cloudflare?
Cloudflare generally only forwards the data that is controlled by website operators. The content is therefore not determined by Cloudflare, but always by the website operator itself. In addition, Cloudflare may collect certain information about the use of our website and processes data that is sent by us or for which Cloudflare has received corresponding instructions. In most cases, Cloudflare receives data such as IP address, contact and log information, security fingerprints and performance data for websites. Log data helps Cloudflare, for example, to detect new threats. This enables Cloudflare to ensure a high level of security protection for our website. Cloudflare processes this data as part of its services in compliance with applicable laws. This of course also includes the General Data Protection Regulation (GDPR). Cloudflare also works with third-party providers. These may only process personal data under the instruction of Cloudflare and in accordance with the data protection policies and other confidentiality and security measures. Cloudflare does not pass on any personal data without our explicit consent.
How long and where are the data stored?
Cloudflare stores your information primarily in the USA and in the European Economic Area. Cloudflare may transfer and access the information described above from all over the world. In general, Cloudflare stores user-level data for domains on the Free, Pro and Business versions for less than 24 hours. For Enterprise domains that have activated Cloudflare Logs (formerly Enterprise LogShare or ELS), the data can be stored for up to 7 days. However, if IP addresses trigger security warnings at Cloudflare, there may be exceptions to the storage period stated above.
How can I delete my data or prevent data storage?
Cloudflare only retains data logs for as long as necessary, and in most cases this data is deleted again within 24 hours. Cloudflare also does not store any personal data, such as your IP address. However, there is information that Cloudflare stores indefinitely as part of its permanent logs in order to improve the overall performance of Cloudflare Resolver and to detect any security risks. You can find out exactly which permanent logs are stored at https://www.cloudflare.com/application/privacypolicy/. All data that Cloudflare collects (temporarily or permanently) is cleansed of all personal data. In addition, all permanent logs are anonymised by Cloudflare.
In its privacy policy, Cloudflare states that it is not responsible for the content it receives. If, for example, you ask Cloudflare whether it can update or delete your content, Cloudflare will generally refer you to us as the website operator. You can also completely prevent the entire collection and processing of your data by Cloudflare by deactivating the execution of script code in your browser or by integrating a script blocker into your browser.
Legal basis
If you have consented to the use of Cloudflare, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Cloudflare.
We also have a legitimate interest in using Cloudflare to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Cloudflare if you have given your consent.
Cloudflare also processes your data in the USA, among other places. Cloudflare is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Cloudflare uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Cloudflare undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
You can find out more about the standard contractual clauses and the data processed through the use of Cloudflare in the privacy policy at https://www.cloudflare.com/de-de/privacypolicy/.
jQuery CDN Privacy Policy
| jQuery CDN Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Optimisation of our service (to enable the website to load faster) 📓 Processed data: Data such as your IP address You can find more details on this further below in this privacy policy. 📅 Storage period: in most cases, the data is stored until it is no longer required for the provision of the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is jQuery?
In order to deliver our website and all our individual subpages (web pages) to you quickly and smoothly on different devices, we use services of jQuery CDN from the company jQuery Foundation. jQuery is distributed via the Content Delivery Network (CDN) of the American software company StackPath (LCC 2012 McKinney Ave. Suite 1100, Dallas, TX 75201, USA). Through this service, your personal data is stored, managed and processed. In this privacy policy, we go into more detail about which of your data is processed through the use of jQuery CDN.
A Content Delivery Network (CDN) is a network of regionally distributed servers that are connected to each other via the internet. Through this network, content, especially very large files, can be delivered quickly even during heavy load peaks. jQuery creates a copy of our website on its servers. This allows our website to be delivered as quickly as possible. This means that data transmission to your browser is shortened by a CDN.
Why do we use jQuery on our website?
Of course, we want to offer you a comprehensive and well-functioning service with our website. This also includes a fast website. With jQuery, our website can load much faster for you. The use of jQuery is particularly helpful for users from abroad, since in this case the page can be delivered from a server nearby.
What data is processed by jQuery?
jQuery uses JavaScript libraries in order to be able to deliver our website content swiftly. For this purpose, a CDN server loads the necessary files. As soon as a connection to the CDN server is established, your IP address is collected and stored. This only happens if this data has not already been stored in your browser from a previous website visit.
The StackPath privacy policy expressly mentions that StackPath uses aggregated and anonymised data from various services (such as jQuery) to enhance security and for its own services. However, this data cannot be used to identify you as a person.
How long and where are the data stored?
jQuery or StackPath has servers distributed in various countries, and your data may therefore be stored both in America and in the European Economic Area. StackPath retains personal data processed on our behalf for as long as is required to provide the services offered and as is necessary to comply with legal obligations, resolve disputes and enforce agreements.
Right to object
You always have the right to information about, rectification and erasure of your personal data. If you have any questions, you can also contact the persons responsible at jQuery at any time.
If you do not want any data transfer to take place, you always have the option of installing JavaScript blockers such as https://www.ghostery.com/ or noscript.net. However, you can also simply deactivate the execution of JavaScript code in your browser. If you decide to deactivate JavaScript code, the usual functions will also change. For example, a website will no longer load as quickly.
Legal basis
If you have consented to the use of jQuery CDN, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by jQuery CDN.
We also have a legitimate interest in using jQuery CDN to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool if you have given your consent.
StackPath also processes your data in the USA, among other places. StackPath is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, StackPath uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are model templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, StackPath undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
You can find the StackPath data processing terms (Data Protection Addendum), which correspond to the standard contractual clauses, at https://www.stackpath.com/legal/data-processing-addendum.
You can find more information on data protection at StackPath at https://www.stackpath.com/legal/privacy-statement and on jQuery at https://prismic-io.s3.amazonaws.com/openjsf/ba00b254-685f-4e54-b1ca-17984b0f3e55_OpenJS-Foundation-Privacy-Policy-2019-11-15.pdf.
jsdelivr.com-CDN Privacy Policy
| jsdelivr.com-CDN Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Optimisation of our service (to enable the website to load faster) 📓 Processed data: Data such as your IP address, browser type, browser version, which web page is loaded, or the time and date of the page visit You can find more details on this further below in this privacy policy. 📅 Storage period: in most cases, the data is stored until it is no longer required for the provision of the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is jsdelivr.com-CDN?
So that we can deliver our individual web pages to you quickly and flawlessly on all different devices, we use the open-source services of jsdelivr.com from the Polish software company ProspectOne, Królewska 65A/1, 30-081, Kraków, Poland. This is a Content Delivery Network (CDN). This is a network of regionally distributed servers that are connected via the internet. This allows content, especially large files, to be delivered quickly and optimally even during heavy load peaks.
Why do we use jsdelivr.com-CDN?
Of course, we want to offer you a comprehensive and well-functioning service with our website. This also includes a fast website. With jsdelivr.com-CDN, our website can load much faster for you. The use of jsdelivr.com-CDN is particularly helpful for users from abroad, since in this case the page can be delivered from a server nearby.
What data is processed by jsdelivr.com-CDN?
jsDelivr is designed so that JavaScript libraries hosted on npm and Github servers can be downloaded. However, WordPress plugins can also be loaded, provided they are hosted on WordPress.org. In order to provide this service, your browser may send personal data to jsdelivr.com. jsDelivr may therefore collect and store user data such as IP address, browser type, browser version, which web page is loaded, or the time and date of the page visit. The privacy policy of jsdelivr.com expressly states that the company does not use cookies or other tracking services.
How long and where are the data stored?
jsDelivr has servers distributed in various countries, and your data may also be stored outside the European Economic Area. jsDelivr retains personal data processed on our behalf for as long as is required to provide the services offered and as is necessary to comply with legal obligations, resolve disputes and enforce agreements.
Right to object
You always have the right to information about, rectification and erasure of your personal data. If you have any questions, you can also contact the persons responsible at jsdelivr.com-CDN at any time.
If you want to prevent this data transfer, you can install a JavaScript blocker (see, for example, https://noscript.net/). Please note, however, that the website will then no longer be able to offer the usual service (such as fast loading speed).
Legal basis
If you have consented to the use of jsdelivr.com-CDN, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by jsdelivr.com-CDN.
We also have a legitimate interest in using jsdelivr.com-CDN to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool if you have given your consent.
You can find more detailed information on data processing by the software service jsDelivr in the company's privacy policy at https://www.jsdelivr.com/terms/privacy-policy-jsdelivr-net.
Cookie Consent Management Platform Introduction
| Cookie Consent Management Platform Summary 👥 Data subjects: Website visitors 🤝 Purpose: Obtaining and managing consent to certain cookies and thus to the use of certain tools 📓 Processed data: Data for managing the configured cookie settings, such as IP address, time of consent, type of consent, individual consents. You can find more details on this in the respective tool used. 📅 Storage period: Depends on the tool used; you should expect periods of several years ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is a Cookie Consent Management Platform?
On our website, we use Consent Management Platform (CMP) software that makes it easier for us and for you to handle the scripts and cookies used correctly and securely. The software automatically creates a cookie pop-up, scans and controls all scripts and cookies, provides you with the cookie consent required under data protection law and helps us and you keep track of all cookies. With most cookie consent management tools, all existing cookies are identified and categorised. You as a website visitor then decide for yourself whether and which scripts and cookies you allow or do not allow. The following graphic illustrates the relationship between browser, web server and CMP.
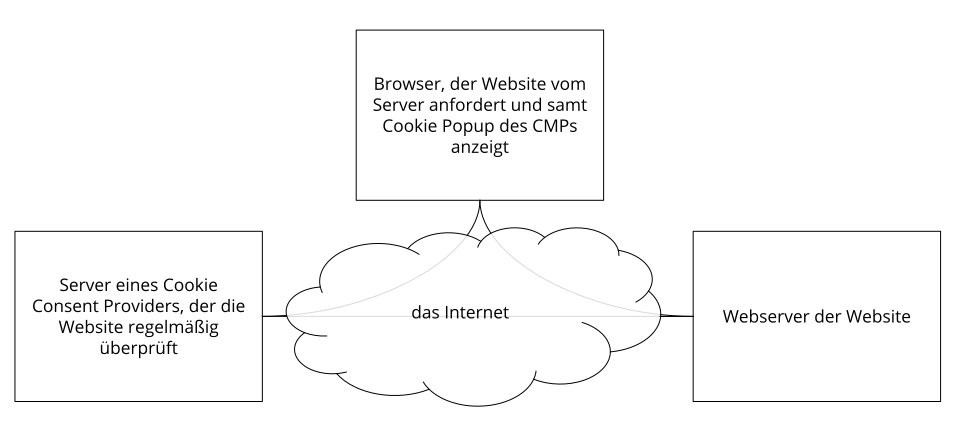
Why do we use a cookie management tool?
Our goal is to offer you the best possible transparency in the area of data protection. Furthermore, we are also legally obliged to do so. We want to inform you as well as possible about all tools and all cookies that can store and process your data. It is also your right to decide for yourself which cookies you accept and which you do not. In order to grant you this right, we first need to know exactly which cookies have ended up on our website at all. Thanks to a cookie management tool that regularly scans the website for all existing cookies, we know about all cookies and can provide you with information about them in compliance with the GDPR. You can then accept or reject cookies via the consent system.
What data is processed?
Within our cookie management tool, you can manage each individual cookie yourself and have full control over the storage and processing of your data. The declaration of your consent is stored so that we do not have to ask you again each time you visit our website and so that we can also prove your consent where required by law. This is stored either in an opt-in cookie or on a server. The storage period of your cookie consent varies depending on the provider of the cookie management tool. In most cases, this data (such as pseudonymous user ID, time of consent, details of the cookie categories or tools, browser, device information) is stored for up to two years.
Duration of data processing
We will inform you about the duration of the data processing further below, provided we have further information on this. In general, we only process personal data for as long as is strictly necessary to provide our services and products. Data stored in cookies is stored for different lengths of time. Some cookies are deleted as soon as you leave the website, while others may be stored in your browser for several years. The exact duration of the data processing depends on the tool used; in most cases you should expect a storage period of several years. The respective privacy policies of the individual providers usually contain precise information on the duration of the data processing.
Right to object
You also have the right and the option to withdraw your consent to the use of cookies at any time. This works either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting the cookies in your browser.
Information on specific cookie management tools, where available, can be found in the following sections.
Legal basis
If you consent to cookies, your personal data will be processed and stored via these cookies. If we are permitted to use cookies on the basis of your consent (Article 6(1)(a) GDPR), this consent is at the same time the legal basis for the use of cookies and the processing of your data. In order to be able to manage consent to cookies and to enable you to give your consent, cookie consent management platform software is used. The use of this software enables us to operate the website efficiently and in compliance with the law, which constitutes a legitimate interest (Article 6(1)(f) GDPR).
Cookiebot Privacy Policy
| Cookiebot Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Obtaining consent to certain cookies and thus to the use of certain tools 📓 Processed data: Data for managing the configured cookie settings, such as IP address, time of consent, type of consent, individual consents. You can find more details on this in the respective tool used. 📅 Storage period: the data is deleted after one year ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Cookiebot?
On our website, we use functions of the provider Cookiebot. The company behind Cookiebot is Cybot A/S, Havnegade 39, 1058 Copenhagen, DK. Among other things, Cookiebot offers us the option of providing you with a comprehensive cookie notice (also known as a cookie banner or cookie notice). Through the use of this function, your data may be sent to, stored and processed by Cookiebot or Cybot. In this privacy policy, we inform you why we use Cookiebot, which data is transferred and how you can prevent this data transfer.
Cookiebot is a software product of the company Cybot. The software automatically creates a GDPR-compliant cookie notice for our website visitors. In addition, the technology behind Cookiebot scans, controls and evaluates all cookies and tracking measures on our website.
Why do we use Cookiebot on our website?
We take data protection very seriously. We want to show you exactly what is happening on our website and which of your data is stored. Cookiebot helps us to maintain a good overview of all our cookies (first-party and third-party cookies). This enables us to inform you precisely and transparently about the use of cookies on our website. You always receive an up-to-date, data-protection-compliant cookie notice and decide for yourself which cookies you allow and which you do not.
What data is stored by Cookiebot?
If you allow cookies, the following data is transferred to, stored and processed by Cybot.
- IP address (in anonymised form, the last 3 digits are set to 0)
- Date and time of your consent
- our website URL
- technical browser data
- encrypted, anonymous key
- the cookies you have allowed (as proof of consent)
The following cookies are set by Cookiebot if you have consented to the use of cookies:
Name: CookieConsent
Value: {stamp:’P7to4eNgIHvJvDerjKneBsmJQd9122821163-2
Purpose: This cookie stores your consent status. This enables our website to read and follow the current status on future visits as well.
Expiry date: after one year
Name: CookieConsentBulkTicket
Value: kDSPWpA%2fjhljZKClPqsncfR8SveTnNWhys5NojaxdFYBPjZ2PaDnUw%3d%3122821163-6
Purpose: This cookie is set if you allow all cookies and have thus activated a “bulk consent”. The cookie then stores its own random and unique ID.
Expiry date: after one year
Note: Please bear in mind that this is an exemplary list and we cannot claim it to be complete. In the cookie declaration at https://www.cookiebot.com/de/cookie-declaration/ you can see which other cookies may be used.
According to Cybot's privacy policy, the company does not sell personal data. However, Cybot does pass on data to trusted third parties or subcontractors who help the company achieve its own business objectives. Data is also passed on if this is required by law.
How long and where are the data stored?
All data collected is transferred, stored and forwarded exclusively within the European Union. The data is stored in an Azure data centre (the cloud provider is Microsoft). At https://azure.microsoft.com/de-de/explore/global-infrastructure/geographies/ you can find out more about all “Azure regions”. All user data is deleted by Cookiebot 12 months after registration (cookie consent) or immediately after termination of the Cookiebot service.
How can I delete my data or prevent data storage?
You have the right to access your personal data and also to delete it at any time. You can prevent data collection and storage, for example, by rejecting the use of cookies via the cookie notice. Your browser offers a further option to prevent data processing or to manage it according to your wishes. Cookie management works slightly differently depending on the browser. In the “Cookies” section you will find the corresponding links to the respective instructions for the best-known browsers.
Legal basis
If you consent to cookies, your personal data will be processed and stored via these cookies. If we are permitted to use cookies on the basis of your consent (Article 6(1)(a) GDPR), this consent is at the same time the legal basis for the use of cookies and the processing of your data. In order to be able to manage consent to cookies and to enable you to give your consent, Cookiebot is used. The use of this software enables us to operate the website efficiently and in compliance with the law, which constitutes a legitimate interest (Article 6(1)(f) GDPR).
If you would like to find out more about the data protection policies of “Cookiebot” or the company behind it, Cybot, we recommend that you read the data protection policies at https://www.cookiebot.com/de/privacy-policy/.
Cookiefirst Privacy Policy
We use Cookiefirst, a cookie consent manager tool, on our website. The service provider is the Dutch company Digital Data Solutions B.V., Plantage Middenlaan 42a, 1018DH, Amsterdam, Netherlands.
You can find out more about the data processed through the use of Cookiefirst in the Privacy Policy at https://cookiefirst.com/legal/general-terms-conditions/.
External Online Platforms Introduction
| External Online Platforms Privacy Policy Summary 👥 Data subjects: Website visitors or visitors to the external online platforms 🤝 Purpose: Presentation and optimisation of our services, contact with visitors and prospective customers 📓 Data processed: Data such as telephone numbers, e-mail addresses, contact details, data on user behaviour, information about your device and your IP address. You can find more details on this at the respective platform used. 📅 Storage period: depends on the platforms used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are external online platforms?
In order to be able to offer our services or products outside our website as well, we also use external platforms. These are usually online marketplaces such as Amazon or eBay. In addition to our own responsibility for data protection, the privacy policies of the external platforms we use also apply. This is particularly the case when our products are purchased via the platform, i.e. when a payment transaction takes place. Furthermore, most platforms also use your data to optimise their own marketing measures. For example, with the help of the data collected, the platform can tailor advertisements precisely to the interests of customers and website visitors.
Why do we use external online platforms?
In addition to our website, we also want to offer our services on other platforms in order to bring our offering closer to more customers. External online marketplaces such as Amazon, eBay or Digistore24 provide large sales websites that present our products to people who may not know our website. It may also happen that elements embedded on our site lead to an external online platform. Data processed and stored by the online platform used serves the company, on the one hand, to log the payment transaction and, on the other hand, to be able to carry out web analyses.
The aim of these analyses is to be able to develop more precise and personalised marketing and advertising strategies. Depending on your behaviour on a platform, the evaluated data can be used to draw appropriate conclusions about your interests and to create so-called user profiles. This also enables the platforms to present you with tailored advertisements or products. For this purpose, cookies are usually set in your browser that store data on your usage behaviour.
Please note that when you use the platforms or our embedded elements, your data may also be processed outside the European Union, as online platforms such as Amazon or eBay are American companies. As a result, you may no longer be able to claim or enforce your rights regarding your personal data as easily.
What data is processed?
Exactly which data is stored and processed depends on the respective external platform. Usually, however, this is data such as telephone numbers, e-mail addresses, data you enter in a contact form, user data such as which buttons you click and when you visited which pages, information about your device and your IP address. Most of this data is very frequently stored in cookies. If you have your own profile on an external platform and are logged in there, data may be linked to that profile. The data collected is stored and processed on the servers of the platforms used. You can find out exactly how an external platform stores, manages and processes data in its respective privacy policy. If you have any questions about data storage and data processing or wish to exercise the corresponding rights, we recommend that you contact the platform directly.
Duration of data processing
We will inform you about the duration of data processing below, provided we have further information on this. For example, Amazon stores data until it is no longer needed for its own purposes. In general, we only process personal data for as long as is strictly necessary to provide our services and products.
Right to object
You also have the right and the option to withdraw your consent to the use of cookies at any time. This can be done either via our cookie management tool or via opt-out functions of the respective external platform. Furthermore, you can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser.
Since cookies may be used, we also recommend that you read our general privacy policy on cookies. To find out exactly which of your data is stored and processed, you should read the privacy policies of the respective external platforms.
Legal basis
If you have consented to your data being processed and stored by external platforms, this consent constitutes the legal basis for data processing (Art. 6(1)(a) GDPR). In principle, where consent has been given, your data is also stored and processed on the basis of a legitimate interest (Art. 6(1)(f) GDPR) in fast and good communication with you or other customers and business partners. If we have embedded elements of external platforms on our website, we nevertheless only use them insofar as you have given your consent.
Information on specific external platforms – where available – can be found in the following sections.
Audio & Video Introduction
| Audio & Video Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Optimisation of our services 📓 Data processed: Data such as contact details, data on user behaviour, information about your device and your IP address may be stored. You can find more details on this further below in the corresponding privacy texts. 📅 Storage period: data generally remains stored for as long as it is necessary for the purpose of the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are audio and video elements?
We have embedded audio and video elements on our website so that you can, for example, watch videos or listen to music/podcasts directly via our website. The content is provided by service providers. All content is therefore also obtained from the respective servers of the providers.
These are embedded functional elements of platforms such as YouTube, Vimeo or Spotify. The use of these portals is generally free of charge, but paid content may also be published. With the help of these embedded elements, you can listen to or watch the respective content via our website.
If you use audio or video elements on our website, personal data about you may also be transmitted to, processed and stored by the service providers.
Why do we use audio & video elements on our website?
Of course, we want to provide you with the best possible offering on our website. And we are aware that content is no longer conveyed merely through text and static images. Instead of simply giving you a link to a video, we offer you audio and video formats directly on our website that are entertaining or informative and, ideally, even both. This extends our service and makes it easier for you to access interesting content. Thus, in addition to our texts and images, we also offer video and/or audio content.
Which data is stored by audio & video elements?
When you call up a page on our website that has, for example, an embedded video, your server connects to the server of the service provider. In the process, data about you is also transmitted to the third-party provider and stored there. Some data is collected and stored regardless of whether or not you have an account with the third-party provider. This usually includes your IP address, browser type, operating system and other general information about your terminal device. Furthermore, most providers also collect information about your web activity. This includes, for example, session duration, bounce rate, which button you clicked on or via which website you are using the service. All this information is usually stored via cookies or pixel tags (also called web beacons). Pseudonymised data is usually stored in cookies in your browser. You can always find out exactly which data is stored and processed in the privacy policy of the respective provider.
Duration of data processing
You can find out exactly how long the data is stored on the third-party providers' servers either further below in the privacy text of the respective tool or in the provider's privacy policy. In principle, personal data is only ever processed for as long as is strictly necessary to provide our services or products. As a rule, this also applies to third-party providers. In most cases, you can assume that certain data will be stored on the third-party providers' servers for several years. Data, especially in cookies, may be stored for varying lengths of time. Some cookies are deleted as soon as you leave the website, while others may remain stored in your browser for several years.
Right to object
You also have the right and the option to withdraw your consent to the use of cookies or third-party providers at any time. This can be done either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser. The lawfulness of processing carried out up to the time of withdrawal remains unaffected.
Since cookies are usually also used by the embedded audio and video functions on our site, you should also read our general privacy policy on cookies. You can find more detailed information on the handling and storage of your data in the privacy policies of the respective third-party providers.
Legal basis
If you have consented to your data being processed and stored by embedded audio and video elements, this consent constitutes the legal basis for data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and good communication with you or other customers and business partners. We nevertheless only use the embedded audio and video elements insofar as you have given your consent.
YouTube Privacy Policy
| YouTube Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Optimisation of our services 📓 Data processed: Data such as contact details, data on user behaviour, information about your device and your IP address may be stored. You can find more details on this further below in this privacy policy. 📅 Storage period: data generally remains stored for as long as it is necessary for the purpose of the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is YouTube?
We have embedded YouTube videos on our website. This allows us to present interesting videos to you directly on our site. YouTube is a video portal that has been a subsidiary of Google since 2006. The video portal is operated by YouTube, LLC, 901 Cherry Ave., San Bruno, CA 94066, USA. When you call up a page on our website that has an embedded YouTube video, your browser automatically connects to the servers of YouTube or Google. In the process, various data is transmitted (depending on the settings). Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all data processing in the European area.
In the following, we would like to explain in more detail which data is processed, why we have embedded YouTube videos and how you can manage or delete your data.
On YouTube, users can watch, rate, comment on and upload videos themselves free of charge. Over the past few years, YouTube has become one of the most important social media channels worldwide. So that we can display videos on our website, YouTube provides a code snippet that we have embedded on our site.
Why do we use YouTube videos on our website?
YouTube is the video platform with the most visitors and the best content. We strive to offer you the best possible user experience on our website. And of course, interesting videos must not be missing. With the help of our embedded videos, we provide you with further helpful content in addition to our texts and images. In addition, our website is found more easily on the Google search engine thanks to the embedded videos. Even when we run advertisements via Google Ads, Google can – thanks to the data collected – really only show these ads to people who are interested in our offers.
Which data is stored by YouTube?
As soon as you visit one of our pages that has an embedded YouTube video, YouTube sets at least one cookie that stores your IP address and our URL. If you are logged into your YouTube account, YouTube can usually assign your interactions on our website to your profile with the help of cookies. This includes data such as session duration, bounce rate, approximate location, and technical information such as browser type, screen resolution or your internet provider. Further data may include contact details, any ratings, the sharing of content via social media or adding to your favourites on YouTube.
If you are not logged into a Google account or a YouTube account, Google stores data with a unique identifier linked to your device, browser or app. In this way, for example, your preferred language setting is retained. However, a lot of interaction data cannot be stored because fewer cookies are set.
In the following list, we show cookies that were set in a test in the browser. On the one hand, we show cookies that are set without a logged-in YouTube account. On the other hand, we show cookies that are set with a logged-in account. The list cannot claim to be complete, as user data always depends on interactions on YouTube.
Name: YSC
Value: b9-CV6ojI5Y122821163-1
Purpose: This cookie registers a unique ID in order to store statistics on the video viewed.
Expiry date: after end of session
Name: PREF
Value: f1=50000000
Purpose: This cookie also registers your unique ID. Via PREF, Google receives statistics on how you use YouTube videos on our website.
Expiry date: after 8 months
Name: GPS
Value: 1
Purpose: This cookie registers your unique ID on mobile devices in order to track your GPS location.
Expiry date: after 30 minutes
Name: VISITOR_INFO1_LIVE
Value: 95Chz8bagyU
Purpose: This cookie attempts to estimate the user's bandwidth on our websites (with an embedded YouTube video).
Expiry date: after 8 months
Further cookies that are set when you are logged in with your YouTube account:
Name: APISID
Value: zILlvClZSkqGsSwI/AU1aZI6HY7122821163-
Purpose: This cookie is used to create a profile of your interests. The data is used for personalised advertisements.
Expiry date: after 2 years
Name: CONSENT
Value: YES+AT.de+20150628-20-0
Purpose: This cookie stores the status of a user's consent to the use of various Google services. CONSENT also serves security purposes, to verify users and protect user data from unauthorised attacks.
Expiry date: after 19 years
Name: HSID
Value: AcRwpgUik9Dveht0I
Purpose: This cookie is used to create a profile of your interests. This data helps to display personalised advertising.
Expiry date: after 2 years
Name: LOGIN_INFO
Value: AFmmF2swRQIhALl6aL…
Purpose: This cookie stores information about your login data.
Expiry date: after 2 years
Name: SAPISID
Value: 7oaPxoG-pZsJuuF5/AnUdDUIsJ9iJz2vdM
Purpose: This cookie works by uniquely identifying your browser and device. It is used to create a profile of your interests.
Expiry date: after 2 years
Name: SID
Value: oQfNKjAsI122821163-
Purpose: This cookie stores your Google account ID and your last login time in digitally signed and encrypted form.
Expiry date: after 2 years
Name: SIDCC
Value: AN0-TYuqub2JOcDTyL
Purpose: This cookie stores information about how you use the website and which advertising you may have seen before visiting our site.
Expiry date: after 3 months
How long and where are the data stored?
The data that YouTube receives from you and processes is stored on Google servers. Most of these servers are located in America. At https://www.google.com/about/datacenters/locations/?hl=de you can see exactly where Google's data centres are located. Your data is distributed across the servers. This makes the data quicker to retrieve and better protected against manipulation.
Google stores the data collected for different lengths of time. Some data can be deleted by you at any time, other data is deleted automatically after a limited period, and still other data is stored by Google for a longer period. Some data (such as items from “My Activity”, photos or documents, products) that is stored in your Google account remains stored until you delete it. Even if you are not logged into a Google account, you can delete some data that is linked to your device, browser or app.
How can I delete my data or prevent data storage?
In principle, you can delete data in your Google account manually. With the automatic deletion function for location and activity data introduced in 2019, information is stored – depending on your choice – for either 3 or 18 months and then deleted.
Regardless of whether or not you have a Google account, you can configure your browser so that cookies from Google are deleted or deactivated. This works in different ways depending on which browser you use. In the “Cookies” section you will find the corresponding links to the respective instructions for the most popular browsers.
If you generally do not want any cookies, you can set up your browser so that it always informs you when a cookie is about to be set. This allows you to decide for each individual cookie whether to allow it or not.
Legal basis
If you have consented to your data being processed and stored by embedded YouTube elements, this consent constitutes the legal basis for data processing (Art. 6(1)(a) GDPR). In principle, your data is also stored and processed on the basis of our legitimate interest (Art. 6(1)(f) GDPR) in fast and good communication with you or other customers and business partners. We nevertheless only use the embedded YouTube elements insofar as you have given your consent. YouTube also sets cookies in your browser in order to store data. We therefore recommend that you read our privacy text on cookies carefully and look at the privacy policy or the cookie policies of the respective service provider.
YouTube also processes your data in the USA, among other places. YouTube or Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
Since YouTube is a subsidiary of Google, there is a joint privacy policy. If you would like to learn more about how your data is handled, we recommend the privacy policy at https://policies.google.com/privacy?hl=de.
YouTube Subscribe Button Privacy Policy
We have embedded the YouTube Subscribe Button (German: „Abonnieren-Button“) on our website. You can usually recognise the button by the classic YouTube logo. The logo shows the words “Subscribe” or “YouTube” in white lettering against a red background and, to the left of them, the white “play symbol”. However, the button may also be displayed in a different design.
Our YouTube channel regularly offers you funny, interesting or exciting videos. With the embedded “Subscribe button”, you can subscribe to our channel directly from our website and do not have to call up the YouTube website separately. In this way, we want to make access to our comprehensive content as easy as possible for you. Please note that YouTube may thereby store and process data about you.
If you see an embedded subscribe button on our site, YouTube – according to Google – sets at least one cookie. This cookie stores your IP address and our URL. YouTube can also obtain information about your browser, your approximate location and your default language in this way. In our test, the following four cookies were set without being logged into YouTube:
Name: YSC
Value: b9-CV6ojI5122821163Y
Purpose: This cookie registers a unique ID in order to store statistics on the video viewed.
Expiry date: after end of session
Name: PREF
Value: f1=50000000
Purpose: This cookie also registers your unique ID. Via PREF, Google receives statistics on how you use YouTube videos on our website.
Expiry date: after 8 months
Name: GPS
Value: 1
Purpose: This cookie registers your unique ID on mobile devices in order to track your GPS location.
Expiry date: after 30 minutes
Name: VISITOR_INFO1_LIVE
Value: 12282116395Chz8bagyU
Purpose: This cookie attempts to estimate the user's bandwidth on our websites (with an embedded YouTube video).
Expiry date: after 8 months
Note: These cookies were set after a test and cannot claim to be complete.
If you are logged into your YouTube account, YouTube can store many of your actions/interactions on our website with the help of cookies and assign them to your YouTube account. In this way, YouTube receives information such as how long you browse our site, which browser type you use, which screen resolution you prefer or which actions you carry out.
YouTube uses this data, on the one hand, to improve its own services and offers and, on the other hand, to provide analyses and statistics for advertisers (who use Google Ads).
Web Design Introduction
| Web Design Privacy Policy Summary 👥 Data subjects: Website visitors 🤝 Purpose: Improving the user experience 📓 Data processed: Which data is processed depends heavily on the services used. Usually, this includes IP address, technical data, language settings, browser version, screen resolution and name of the browser. You can find more details on this in the respective web design tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is web design?
We use various tools on our website that serve our web design. Contrary to popular belief, web design is not only about making our website look attractive, but also about functionality and performance. But of course, the appropriate look of a website is also one of the major goals of professional web design. Web design is a sub-area of media design and deals with the visual as well as the structural and functional design of a website. The aim is to use web design to improve your experience on our website. In web design jargon, this is referred to as user experience (UX) and usability. User experience refers to all the impressions and experiences that the website visitor has on a website. A sub-aspect of user experience is usability. This concerns the user-friendliness of a website. Particular importance is attached here to content, subpages or products being clearly structured so that you can find what you are looking for easily and quickly. In order to offer you the best possible experience on our website, we also use so-called web design tools from third-party providers. In this privacy policy, the category “web design” therefore covers all services that improve the design of our website. These may include, for example, fonts, various plugins or other embedded web design functions.
Why do we use web design tools?
How you take in information on a website depends very much on the structure, functionality and visual perception of the website. For this reason, good and professional web design has become increasingly important for us too. We are constantly working on improving our website and also regard this as an extended service for you as a website visitor. Furthermore, an attractive and well-functioning website also has economic advantages for us. After all, you will only visit us and make use of our offers if you feel completely comfortable.
Which data is stored by web design tools?
When you visit our website, web design elements may be embedded in our pages that may also process data. Exactly which data is involved naturally depends heavily on the tools used. Further below you can see exactly which tools we use for our website. For more detailed information on data processing, we also recommend that you read the respective privacy policy of the tools used. There you will usually find out which data is processed, whether cookies are used and how long the data is retained. Fonts such as Google Fonts, for example, also automatically transmit information such as language settings, IP address, browser version, browser screen resolution and name of the browser to the Google servers.
Duration of data processing
How long data is processed is very individual and depends on the web design elements used. If cookies are used, for example, the retention period may be just one minute but may also be a few years. Please inform yourself about this. For this purpose, we recommend on the one hand our general text section on cookies and on the other hand the privacy policies of the tools used. There you will usually find out exactly which cookies are used and which information is stored in them. Google Font files, for example, are stored for one year. This is intended to improve the loading time of a website. In principle, data is only ever retained for as long as is necessary to provide the service. In the case of statutory requirements, data may also be stored for longer.
Right to object
You also have the right and the option to withdraw your consent to the use of cookies or third-party providers at any time. This works either via our cookie management tool or via other opt-out functions. You can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser. With web design elements (mostly fonts), however, there is also data that cannot be deleted quite so easily. This is the case when data is automatically collected directly upon accessing a page and transmitted to a third-party provider (such as Google). In that case, please contact the support of the respective provider. In the case of Google, you can reach support at https://support.google.com/?hl=de.
Legal basis
If you have consented to the use of web design tools, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when data is collected by web design tools. In addition, we have a legitimate interest in improving the web design on our website. After all, only then can we provide you with an attractive and professional web offering. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use web design tools insofar as you have given your consent. We would definitely like to emphasise this once again here.
Information on specific web design tools – where available – can be found in the following sections.
Adobe Fonts Privacy Policy
We use Adobe Fonts, a web font hosting service, on our website. The service provider is the American company Adobe Inc. For the European region, the Irish company Adobe Systems Software Ireland Companies, 4-6 Riverwalk, Citywest Business Campus, Dublin 24, Ireland, is responsible.
Adobe also processes your data in the USA, among other places. Adobe is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Adobe uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCCs) are model templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Adobe undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find more information on the standard contractual clauses at Adobe at https://www.adobe.com/at/privacy/eudatatransfers.html.
You can find out more about the data processed through the use of Adobe Fonts in the privacy policy at https://www.adobe.com/at/privacy.html .
Font Awesome Privacy Policy
| Font Awesome Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service 📓 Data processed: such as IP address and which icon files are loaded You can find more details on this further below in this privacy policy. 📅 Storage period: files in identifiable form are stored for a few weeks ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Font Awesome?
We use Font Awesome by the American company Fonticons (307 S. Main St., Suite 202, Bentonville, AR 72712, USA) on our website. When you access one of our web pages, the Font Awesome web font (specifically icons) is loaded via the Font Awesome Content Delivery Network (CDN). This ensures that texts, fonts and icons are displayed appropriately on every end device. In this privacy policy, we go into more detail about data storage and data processing by this service.
Icons play an increasingly important role for websites. Font Awesome is a web font developed specifically for web designers and web developers. With Font Awesome, icons can, for example, be scaled and coloured as desired using the stylesheet language CSS. They thus replace old image icons. Font Awesome CDN is the easiest way to load the icons or fonts onto your website. To do this, we only had to embed a small line of code in our website.
Why do we use Font Awesome on our website?
Font Awesome allows content on our website to be presented more effectively. This makes it easier for you to find your way around our website and to grasp the content. Icons can sometimes even replace entire words and save space. This is particularly practical when we optimise content specifically for smartphones. These icons are inserted as HMTL code instead of as images. This allows us to edit the icons with CSS exactly as we wish. At the same time, Font Awesome also improves our loading speed, because these are only HTML elements and not icon images. All these advantages help us to make the website even clearer, fresher and faster for you.
What data is stored by Font Awesome?
The Font Awesome Content Delivery Network (CDN) is used to load icons and symbols. CDNs are networks of servers distributed worldwide that make it possible to load files quickly from nearby locations. Thus, as soon as you access one of our pages, the corresponding icons are provided by Font Awesome.
In order for the web fonts to be loaded, your browser must establish a connection to the servers of the company Fonticons, Inc. In doing so, your IP address is identified. Font Awesome also collects data about which icon files are downloaded and when. Furthermore, technical data such as your browser version, screen resolution or the time the page was accessed are also transmitted.
This data is collected and stored for the following reasons:
- to optimise content delivery networks
- to detect and fix technical errors
- to protect CDNs from misuse and attacks
- to be able to calculate fees for Font Awesome Pro customers
- to learn about the popularity of icons
- to know which computer and which software you are using
If your browser does not allow web fonts, a standard font of your PC is used automatically. To the best of our current knowledge, no cookies are set. We are in contact with the data protection department of Font Awesome and will inform you as soon as we learn more.
How long and where are the data stored?
Font Awesome stores data on the use of the Content Delivery Network on servers, including in the United States of America. However, the CDN servers are located worldwide and store user data where you are located. In identifiable form, the data is generally stored for only a few weeks. Aggregated statistics on the use of the CDNs may also be stored for longer. Personal data is not included here.
How can I delete my data or prevent data storage?
To the best of our current knowledge, Font Awesome does not store any personal data via the content delivery networks. If you do not want data about the icons used to be stored, you unfortunately cannot visit our website. If your browser does not allow web fonts, no data is transmitted or stored either. In this case, the standard font of your computer is simply used.
Legal basis
If you have consented to the use of Font Awesome, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when data is collected by Font Awesome.
In addition, we have a legitimate interest in using Font Awesome to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Font Awesome insofar as you have given your consent.
We would like to point out that, in the opinion of the European Court of Justice, there is currently no adequate level of protection for the transfer of data to the USA. Data processing is essentially carried out by Font Awesome. This may result in data not being processed and stored in anonymised form. Furthermore, US government authorities may be able to access individual data. It may also happen that this data is linked to data from other services of Font Awesome for which you have a user account.
If you would like to learn more about Font Awesome and how it handles data, we recommend the privacy policy at https://fontawesome.com/privacy and the help page at https://fontawesome.com/support.
Google Fonts Privacy Policy
| Google Fonts Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service 📓 Data processed: data such as IP address and CSS and font requests You can find more details on this further below in this privacy policy. 📅 Storage period: font files are stored by Google for one year ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are Google Fonts?
We use Google Fonts on our website. These are the “Google fonts” of the company Google Inc. For the European region, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services.
To use Google fonts, you do not need to log in or provide a password. Furthermore, no cookies are stored in your browser. The files (CSS, typefaces/fonts) are requested via the Google domains fonts.googleapis.com and fonts.gstatic.com. According to Google, requests for CSS and fonts are completely separate from all other Google services. If you have a Google account, you need not worry that your Google account data will be transmitted to Google while Google Fonts is being used. Google records the use of CSS (Cascading Style Sheets) and of the fonts used and stores this data securely. We will take a detailed look at exactly how the data storage works below.
Google Fonts (formerly Google Web Fonts) is a directory of over 800 fonts that Google makes available to its users free of charge.
Many of these fonts are published under the SIL Open Font License, while others have been published under the Apache License. Both are free software licences.
Why do we use Google Fonts on our website?
With Google Fonts, we can use fonts on our own website without having to upload them to our own server. Google Fonts is an important building block in keeping the quality of our website high. All Google fonts are automatically optimised for the web, which saves data volume and is a great advantage, especially for use on mobile devices. When you visit our site, the small file size ensures a fast loading time. Furthermore, Google Fonts are secure web fonts. Different image synthesis systems (rendering) in different browsers, operating systems and mobile devices can lead to errors. Such errors can visually distort texts or even entire web pages. Thanks to the fast Content Delivery Network (CDN), there are no cross-platform issues with Google Fonts. Google Fonts supports all common browsers (Google Chrome, Mozilla Firefox, Apple Safari, Opera) and works reliably on most modern mobile operating systems, including Android 2.2+ and iOS 4.2+ (iPhone, iPad, iPod). We therefore use Google Fonts so that we can present our entire online service as attractively and consistently as possible.
What data is stored by Google?
When you visit our website, the fonts are loaded via a Google server. Through this external call, data is transmitted to the Google servers. In this way, Google also recognises that you or your IP address is visiting our website. The Google Fonts API was developed to reduce the use, storage and collection of end-user data to what is necessary for the proper provision of fonts. Incidentally, API stands for “Application Programming Interface” and serves, among other things, as a data transmitter in the software sector.
Google Fonts stores CSS and font requests securely with Google and is therefore protected. Through the collected usage figures, Google can determine how well the individual fonts are received. Google publishes the results on internal analysis pages, such as Google Analytics. In addition, Google also uses data from its own web crawler to determine which websites use Google fonts. This data is published in the Google Fonts BigQuery database. Entrepreneurs and developers use the Google web service BigQuery to be able to examine and move large volumes of data.
It should be borne in mind, however, that with every Google Font request, information such as language settings, IP address, browser version, browser screen resolution and browser name is also automatically transmitted to the Google servers. Whether this data is also stored cannot be clearly determined or is not clearly communicated by Google.
How long and where are the data stored?
Google stores requests for CSS assets for one day on its servers, which are mainly located outside the EU. This enables us to use the fonts with the help of a Google stylesheet. A stylesheet is a style template that can be used to quickly and easily change, for example, the design or font of a website.
The font files are stored by Google for one year. Google's aim in doing so is to fundamentally improve the loading time of websites. When millions of websites refer to the same fonts, they are cached after the first visit and reappear immediately on all other websites visited later. Google sometimes updates font files to reduce file size, increase language coverage and improve design.
How can I delete my data or prevent data storage?
The data that Google stores for one day or one year cannot simply be deleted. The data is automatically transmitted to Google when the page is accessed. In order to have this data deleted prematurely, you must contact Google support at https://support.google.com/?hl=de&tid=122821163. In this case, you can only prevent data storage by not visiting our site.
Unlike other web fonts, Google allows us unrestricted access to all fonts. We can therefore access a sea of fonts without limitation and thus get the best out of our website. You can find more about Google Fonts and other questions at https://developers.google.com/fonts/faq?tid=122821163. Although Google addresses privacy-related matters there, it does not contain truly detailed information about data storage. It is relatively difficult to obtain really precise information about stored data from Google.
Legal basis
If you have consented to the use of Google Fonts, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when data is collected by Google Fonts.
In addition, we have a legitimate interest in using Google Font to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Font insofar as you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
You can also read about which data is generally collected by Google and what this data is used for at https://www.google.com/intl/de/policies/privacy/.
Google Fonts Local Privacy Policy
We use Google Fonts of the company Google Inc. on our website. For the European region, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible. We have integrated the Google fonts locally, i.e. on our web server – not on Google's servers. As a result, there is no connection to Google servers and therefore no data transmission or storage.
What are Google Fonts?
Google Fonts used to be called Google Web Fonts. It is an interactive directory of over 800 fonts that Google provides free of charge. With Google Fonts, one could use fonts without uploading them to one's own server. However, in order to prevent any transfer of information to Google servers in this respect, we have downloaded the fonts to our server. In this way, we act in compliance with data protection law and do not pass on any data to Google Fonts.
Online Map Services Introduction
| Online Map Services Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: improvement of the user experience 📓 Data processed: Which data is processed depends heavily on the services used. In most cases, it is the IP address, location data, search items and/or technical data. You can find more details on this in the respective tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are online map services?
We also use online map services for our website as an extended service. Google Maps is probably the service you are most familiar with, but there are also other providers that specialise in creating digital maps. Such services make it possible to display locations, route plans or other geographical information directly via our website. Thanks to an embedded map service, you no longer have to leave our website in order, for example, to view the route to a location. For the online map to work on our website, map sections are embedded using HTML code. The services can then display road maps, the earth's surface or aerial or satellite images. When you use the embedded map offering, data is also transmitted to the tool used and stored there. This data may also include personal data.
Why do we use online map services on our website?
Generally speaking, our aim is to provide you with a pleasant time on our website. And of course your time is only pleasant if you can easily find your way around our website and find all the information you need quickly and easily. We therefore thought that an online map system could be a significant further optimisation of our service on the website. Without leaving our website, you can easily view route descriptions, locations or even sights with the help of the map system. Of course, it is also extremely practical that you can see at a glance where our headquarters are located, so that you can find your way to us quickly and safely. As you can see, there are simply many advantages, and we clearly regard online map services on our website as part of our customer service.
What data is stored by online map services?
When you open a page on our website that has an embedded online map function, personal data may be transmitted to the respective service and stored there. In most cases, this is your IP address, which can also be used to determine your approximate location. In addition to the IP address, data such as entered search terms and longitude and latitude coordinates are also stored. If, for example, you enter an address for route planning, this data is also stored. The data is not stored by us, but on the servers of the embedded tools. You can imagine it roughly like this: although you are on our website, when you interact with a map service, this interaction actually takes place on their website. To ensure that the service functions properly, at least one cookie is usually also set in your browser. Google Maps, for example, also uses cookies to record user behaviour and thus optimise its own service and be able to display personalised advertising. You can find out more about cookies in our section “Cookies”.
How long and where are the data stored?
Each online map service processes different user data. If further information is available to us, we will inform you about the duration of data processing further below in the corresponding sections on the individual tools. In principle, personal data is only ever retained for as long as is necessary for the provision of the service. Google Maps, for example, stores certain data for a fixed period, while other data you must delete yourself. With Mapbox, for example, the IP address is retained for 30 days and then deleted. As you can see, each tool stores data for different lengths of time. We therefore recommend that you take a close look at the privacy policies of the tools used.
The providers also use cookies to store data on your user behaviour with the map service. You can find more general information on cookies in our section “Cookies”, but the privacy texts of the individual providers will also tell you which cookies may be used. In most cases, however, this is only an exemplary list and is not complete.
Right to object
You always have the option and also the right to access your personal data and also to object to its use and processing. You can also withdraw the consent you have given us at any time. As a rule, the easiest way to do this is via the cookie consent tool. However, there are also other opt-out tools that you can use. You can also manage, delete or deactivate any cookies set by the providers used yourself with just a few mouse clicks. However, it may then happen that some functions of the service no longer work as usual. How you manage cookies in your browser also depends on the browser you use. In the section “Cookies” you will also find links to the instructions for the most important browsers.
Legal basis
If you have consented to the use of an online map service, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when data is collected by an online map service.
In addition, we also have a legitimate interest in using an online map service in order to optimise our service on our website. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). However, we only ever use an online map service if you have given your consent. We definitely want to state this once again at this point.
Information on specific online map services – where available – can be found in the following sections.
Google Maps Privacy Policy
| Google Maps Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service 📓 Data processed: data such as entered search terms, your IP address and also the latitude and longitude coordinates. You can find more details on this further below in this privacy policy. 📅 Storage period: depends on the data stored ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Maps?
We use Google Maps of the company Google Inc. on our website. For the European region, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. With Google Maps, we can show you locations more effectively and thus adapt our service to your needs. Through the use of Google Maps, data is transmitted to Google and stored on Google servers. Here we would like to explain in more detail what Google Maps is, why we use this Google service, what data is stored and how you can prevent this.
Google Maps is an internet map service of the company Google. With Google Maps, you can search online via a PC, a tablet or an app for the exact locations of cities, sights, accommodation or businesses. If businesses are represented on Google My Business, further information about the company is displayed in addition to the location. To show directions, map sections of a location can be embedded in a website using HTML code. Google Maps shows the earth's surface as a road map or as an aerial or satellite image. Thanks to the Street View images and the high-quality satellite images, very precise representations are possible.
Why do we use Google Maps on our website?
All our efforts on this site are aimed at providing you with a useful and meaningful time on our website. By embedding Google Maps, we can provide you with the most important information on various locations. You can see at a glance where our headquarters are located. The directions always show you the best or fastest way to us. You can retrieve directions for routes by car, by public transport, on foot or by bicycle. For us, the provision of Google Maps is part of our customer service.
What data is stored by Google Maps?
In order for Google Maps to be able to offer its service in full, the company must collect and store data from you. This includes, among other things, the search terms entered, your IP address and also the latitude and longitude coordinates. If you use the route planner function, the starting address entered is also stored. However, this data storage takes place on the Google Maps websites. We can only inform you about this but cannot exert any influence. Since we have embedded Google Maps in our website, Google sets at least one cookie (name: NID) in your browser. This cookie stores data about your user behaviour. Google uses this data primarily to optimise its own services and to provide individual, personalised advertising for you.
The following cookie is set in your browser due to the embedding of Google Maps:
Name: NID
Value: 188=h26c1Ktha7fCQTx8rXgLyATyITJ122821163-5
Purpose: NID is used by Google to tailor advertisements to your Google searches. With the help of the cookie, Google “remembers” your most frequently entered search queries or your previous interaction with ads. This way you always receive tailored advertisements. The cookie contains a unique ID that Google uses to collect your personal settings for advertising purposes.
Expiry date: after 6 months
Note: We cannot guarantee the completeness of the information on the stored data. Especially with the use of cookies, changes can never be ruled out. To identify the NID cookie, a separate test page was created on which only Google Maps was embedded.
How long and where are the data stored?
The Google servers are located in data centres all over the world. Most of the servers, however, are located in America. For this reason, your data is also increasingly stored in the USA. Here you can read exactly where the Google data centres are located: https://www.google.com/about/datacenters/locations/?hl=de
Google distributes the data across various storage media. This makes the data quicker to retrieve and better protected against any attempts at manipulation. Each data centre also has special emergency programmes. If, for example, there are problems with Google’s hardware or a natural disaster brings the servers down, the data will still remain quite safely protected.
Google stores some data for a fixed period of time. For other data, Google merely offers the option of deleting it manually. Furthermore, the company also anonymises information (such as advertising data) in server logs by deleting part of the IP address and cookie information after 9 or 18 months respectively.
How can I delete my data or prevent data storage?
With the automatic deletion function for location and activity data introduced in 2019, information on location determination and web/app activity is – depending on your choice – stored for either 3 or 18 months and then deleted. In addition, you can also manually delete this data from your history at any time via your Google account. If you want to prevent your location from being recorded altogether, you must pause the “Web & App Activity” section in your Google account. Click on “Data & personalisation” and then on the option “Activity controls”. Here you can switch the activities on or off.
In your browser, you can also deactivate, delete or manage individual cookies. Depending on which browser you use, this always works slightly differently. Under the section “Cookies” you will find the corresponding links to the respective instructions for the most popular browsers.
If you generally do not want any cookies, you can set up your browser so that it always informs you when a cookie is about to be set. This allows you to decide for each individual cookie whether to allow it or not.
Legal basis
If you have consented to the use of Google Maps, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Google Maps.
We also have a legitimate interest in using Google Maps in order to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Maps insofar as you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
If you would like to learn more about Google’s data processing, we recommend the company’s own privacy policy at https://policies.google.com/privacy?hl=de.
OpenStreetMap Privacy Policy
| OpenStreetMap Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service performance 📓 Data processed: data such as IP address, browser information, your operating system, content of the request, limited location and usage data You can find more details on this further below in this privacy policy. 📅 Storage period: the IP address is deleted after 180 days ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is OpenStreetMap?
We have integrated map sections from the online mapping tool “OpenStreetMap” on our website. This is so-called open-source mapping, which we can access via an API (interface). This function is offered by the OpenStreetMap Foundation, St John’s Innovation Centre, Cowley Road, Cambridge, CB4 0WS, United Kingdom. By using this map function, your IP address is forwarded to OpenStreetMap. In this privacy policy you will learn why we use functions of the OpenStreetMap tool, where which data is stored and how you can prevent this data storage.
The OpenStreetMap project was launched in 2004. The aim of the project is and was to create a free map of the world. Users around the world collect data on, for example, buildings, forests, rivers and roads. Over the years, this has resulted in a comprehensive digital world map created by the users themselves. Of course, the map is not complete, but in most regions it is equipped with a great deal of data.
Why do we use OpenStreetMap on our website?
Our website is first and foremost intended to be helpful to you. And in our view, it is helpful whenever information can be found quickly and easily. On the one hand, this naturally concerns our services and products; on the other hand, further helpful information should also be available to you. That is why we also use the map service OpenStreetMap. This allows us, for example, to show you exactly how to find our company. The map shows you the best way to reach us, and your journey becomes child’s play.
What data is stored by OpenStreetMap?
When you visit one of our web pages that offers OpenStreetMap, user data is transmitted to the service and stored there. OpenStreetMap collects, for example, information about your interactions with the digital map, your IP address, data about your browser, device type, operating system and on which day and at what time you used the service. Tracking software is also used for this purpose to record user interactions. In its own privacy policy, the company specifies the analysis tool “Piwik” in this regard.
The collected data is subsequently accessible to the relevant working groups of the OpenStreetMap Foundation. According to the company, personal data is not passed on to other persons or companies unless this is legally required. The third-party provider Piwik does store your IP address, but in shortened form.
The following cookie may be set in your browser when you interact with OpenStreetMap on our website:
Name: _osm_location
Value: 9.63312%7C52.41500%7C17%7CM
Purpose: The cookie is required to unlock the content of OpenStreetMap.
Expiry date: after 10 years
If you want to view the full-screen map, you will be linked to the OpenStreetMap website. There, the following cookies, among others, may be stored in your browser:
Name: _osm_totp_token
Value: 148253122821163-2
Purpose: This cookie is used to ensure the operation of the map section.
Expiry date: after one hour
Name: _osm_session
Value: 1d9bfa122e0259d5f6db4cb8ef653a1c
Purpose: With the help of this cookie, session information (i.e. user behaviour) can be stored.
Expiry date: after the end of the session
Name: _pk_id.1.cf09
Value: 4a5.1593684142.2.1593688396.1593688396122821163-9
Purpose: This cookie is set by Piwik to store or measure user data such as click behaviour.
Expiry date: after one year
How long and where are the data stored?
The API servers, the databases and the servers of auxiliary services are currently located in the United Kingdom (Great Britain and Northern Ireland) and in the Netherlands. Your IP address and user information, which are stored in shortened form by the web analysis tool Piwik, are deleted again after 180 days.
How can I delete my data or prevent data storage?
You have the right to access your personal data at any time and to object to its use and processing. You can manage, delete or deactivate cookies that may be set by OpenStreetMap in your browser at any time. However, this means that the service will no longer function to its full extent. Managing, deleting or deactivating cookies works slightly differently in each browser. Under the section “Cookies” you will find the corresponding links to the respective instructions for the most popular browsers.
Legal basis
If you have consented to the use of OpenStreetMap, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by OpenStreetMap.
We also have a legitimate interest in using OpenStreetMap in order to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use OpenStreetMap insofar as you have given your consent.
If you would like to learn more about data processing by OpenStreetMap, we recommend the company’s privacy policy at https://wiki.osmfoundation.org/wiki/Privacy_Policy.
Content Search Providers Introduction
| Content Search Providers Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: improvement of the user experience 📓 Data processed: Which data is processed depends heavily on the services used. In most cases, this is the IP address, search interests and/or technical data. You can find more details on this in the respective tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is a content search provider?
By now we have published a great deal of content on our website. And of course we do not want it simply to be forgotten just because it cannot be found. That is why we use a content search provider on our website. You are certainly familiar with large search engines such as Google. A content search provider is essentially also a search engine, which, unlike Google, does not search the entire web for content, but only the website you are on. Via a text field you can enter terms that match the content you are looking for, and the search program finds the desired posts for you. If you use the integrated search function, your personal data may also be processed.
Why do we use a content search provider?
When you look around our website, you will quickly notice how much useful content we have already published over the years. There are real treasures among it, and we want you to be able to find them quickly without a lot of clicking around. With a content search function directly on our website, you can quickly and easily find the content you are looking for with the help of keywords that match the topic you are searching for. This feature is really practical, and we also see it as our task to make your time on our website as pleasant and helpful as possible. That is why we have decided to integrate a program for content search into our website.
What data is processed?
When you use the search function on our website, the integrated content search provider (such as Algolia Places or Giphy) may automatically receive and store data from you. This includes technical data about your browser as well as data such as your IP address, device ID and the search terms entered. Please note that IP addresses are personal data. The providers’ privacy policies state that this information is collected and stored in order to increase security and to improve their own services. The automatically collected usage data, which does not include any personal data and is processed in anonymised form, may also be used for analysis purposes. Some providers also pass on this anonymised data to third parties. To find out more about this, we recommend that you carefully read the specific privacy policies of the individual providers. In order for the services to function properly, cookies are generally also set in your browser. You can learn more about cookies in our general section “Cookies”. Whether and which cookies the individual search tools use can be found – where available – further below or in the corresponding privacy policies of the integrated tools.
How long and where are the data stored?
As a general rule, each content search provider processes different data. Therefore, this general section cannot specifically address the data processing of the individual tools. Usually, however, the services only store personal data for as long as this is necessary for the smooth functioning of the tools. Some services (such as Giphy) also retain personal data for longer if this is required due to legal obligations. Most providers also retain data in depersonalised form for longer. Content search providers may also use cookies to store various data. You can find out more about this in our general section on cookies. If you would like to know about the specific cookies that a search provider uses, we recommend the privacy policy of the providers we use. There you will usually find an exemplary list of the cookies used.
Right to object
Always be aware: if you do not wish it, no personal data of yours may be processed. You always have the right to access your personal data and to object to its use. You can also withdraw your consent at any time via the cookie consent tool or via other opt-out options. You can also very easily manage, delete or deactivate the cookies used yourself via your browser. If you delete cookies, it is possible that some functions of the tool will no longer work. So please do not be surprised by this. How you manage cookies in your browser also depends on the browser you use. In the section “Cookies” you will also find links to the instructions for the most important browsers.
Legal basis
If you have consented to the use of a content search provider, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by a content search provider.
We also have a legitimate interest in using a content search provider in order to optimise the service on our website. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). However, we only ever use a content search provider if you have given your consent. We definitely want to state this once again at this point.
Information on specific content search providers can be found – where available – in the following sections.
Google Custom Search Privacy Policy
| Google Custom Search Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: optimisation of our service performance 📓 Data processed: data such as IP address and search terms entered are stored by Google You can find more details on this further below in this privacy policy. 📅 Storage period: the storage period varies depending on the data stored ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Custom Search?
We have integrated the Google plug-in for custom search on our website. Google is the largest and best-known search engine in the world and is operated by the US company Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible. Through Google Custom Search, your data may be transmitted to Google. In this privacy policy we inform you why we use this plug-in, which data is processed and how you can manage or prevent this data transmission.
The Google Custom Search plug-in is a Google search bar directly on our website. The search takes place as on www.google.com, except that the search results focus on our content and products or on a restricted search scope.
Why do we use Google Custom Search on our website?
A website with a lot of interesting content often becomes so large that one may lose track of it. Over time, a lot of valuable material has accumulated with us too, and as part of our service we want you to find our content as quickly and easily as possible. Google Custom Search makes finding interesting content child’s play. The built-in Google plug-in improves the overall quality of our website and makes searching easier for you.
What data is stored by Google Custom Search?
Through Google Custom Search, your data is only transmitted to Google if you actively use the Google search built into our website. This means that only when you enter a search term in the search bar and then confirm this term (e.g. click on “Enter”) is your IP address, in addition to the search term, sent to Google, stored and processed there. Based on the cookies set (such as 1P_JAR), it can be assumed that Google also receives data on website usage. If, during your visit to our website, you search for content via the built-in Google search function and are logged in to your Google account at the same time, Google can also assign the collected data to your Google account. As the website operator, we have no influence on what Google does with the collected data or how Google processes the data.
The following cookies are set in your browser when you use Google Custom Search and are not logged in with a Google account:
Name: 1P_JAR
Value: 2020-01-27-13122821163-5
Purpose: This cookie collects statistics on website usage and measures conversions. A conversion occurs, for example, when a user becomes a buyer. The cookie is also used to display relevant advertisements to users.
Expiry date: after one month
Name: CONSENT
Value: WP.282f52122821163-9
Purpose: The cookie stores the status of a user’s consent to the use of various Google services. CONSENT also serves security purposes, to verify users and to protect user data from unauthorised attacks.
Expiry date: after 18 years
Name: NID
Value: 196=pwIo3B5fHr-8
Purpose: NID is used by Google to tailor advertisements to your Google searches. With the help of the cookie, Google “remembers” the search queries you have entered or your previous interaction with ads. In this way you always receive tailor-made advertisements.
Expiry date: after 6 months
Note: This list cannot claim to be complete, as Google repeatedly changes its choice of cookies.
How long and where are the data stored?
The Google servers are distributed all over the world. As Google is an American company, most data is stored on American servers. At https://www.google.com/about/datacenters/locations/?hl=de you can see exactly where the Google servers are located.
Your data is distributed across various physical storage media. This makes the data quicker to retrieve and better protected against possible manipulation. Google also has appropriate emergency programmes for your data. If, for example, there are internal technical problems at Google and servers stop working as a result, the risk of a service interruption and data loss nevertheless remains low.
Depending on the type of data involved, Google stores it for different lengths of time. You can delete some data yourself; other data is automatically deleted or anonymised by Google. However, there is also data that Google stores for longer if this is necessary for legal or business reasons.
How can I delete my data or prevent data storage?
Under the data protection law of the European Union, you have the right to obtain information about your data and to have it updated, deleted or restricted. There is some data that you can delete at any time. If you have a Google account, you can delete data on your web activity there or specify that it should be deleted after a certain period of time.
In your browser you also have the option of deactivating, deleting or managing cookies according to your wishes and preferences. Under the section “Cookies” you will find the corresponding links to the respective instructions for the most popular browsers.
Legal basis
If you have consented to the use of Google Custom Search, the legal basis for the corresponding data processing is this consent. Pursuant to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Google Custom Search.
We also have a legitimate interest in using Google Custom Search in order to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Custom Search insofar as you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data complies with European data protection standards even if it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/
We hope we have been able to give you the most important information about data processing by Google. If you would like to learn more about this, we recommend Google’s comprehensive privacy policy at https://policies.google.com/privacy?hl=de.
Miscellaneous Introduction
| Miscellaneous Privacy Policy Summary 👥 Data subjects: website visitors 🤝 Purpose: improvement of the user experience 📓 Data processed: Which data is processed depends heavily on the services used. In most cases, this is the IP address and/or technical data. You can find more details on this in the respective tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What falls under “Miscellaneous”?
The category “Miscellaneous” covers those services that do not fit into any of the categories mentioned above. As a rule, these are various plugins and integrated elements that improve our website. As a rule, these functions are obtained from third-party providers and integrated into our website. Examples include web search services such as Algolia Place, Giphy, Programmable Search Engine or online services for weather data such as OpenWeather.
Why do we use other third-party providers?
With our website, we want to offer you the best web offering in our industry. For a long time now, a website has no longer been merely a business card for companies. Rather, it is a place that should help you find what you are looking for. In order to make our website ever more interesting and helpful for you, we use various services from third-party providers.
What data is processed?
Whenever elements are integrated into our website, your IP address is transmitted to the respective provider, stored and processed there. This is necessary because otherwise the content would not be sent to your browser and consequently would not be displayed correctly. It may also happen that service providers use pixel tags or web beacons. These are small graphics on websites that record a log file and can also create analyses of this file. With the information obtained, the providers can improve their own marketing measures. In addition to pixel tags, such information (such as which button you click or when you access which page) may also be stored in cookies. In addition to analysis data on your web behaviour, technical information such as your browser type or your operating system may also be stored therein. Some providers may also link the data obtained with other internal services or with third-party providers. Each provider handles your data differently. We therefore recommend that you carefully read the privacy policies of the respective services. We generally endeavour to use only services that handle the subject of data protection very carefully.
Duration of data processing
We inform you about the duration of the data processing further below, provided we have further information on this. In general, we only process personal data for as long as is absolutely necessary for the provision of our services and products.
Legal basis
If we ask for your consent and you also consent to our using the service, this constitutes the legal basis for the processing of your data (Art. 6(1)(a) GDPR). In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offering technically and economically. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tools insofar as you have given your consent.
Information on the specific tools can be found – where available – in the following sections.
Explanation of Terms Used
We always endeavour to write our privacy policy as clearly and comprehensibly as possible. However, this is not always easy, particularly with technical and legal topics. It often makes sense to use legal terms (such as personal data) or certain technical expressions (such as cookies, IP address). However, we do not want to use these without explanation. Below you will now find an alphabetical list of important terms used which we may not yet have addressed sufficiently in the privacy policy so far. Where these terms have been taken from the GDPR and are definitions, we will also cite the GDPR texts here and, where appropriate, add our own explanations.
Supervisory authority
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“supervisory authority” means an independent public authority which is established by a Member State pursuant to Article 51;
Explanation: “Supervisory authorities” are always independent state bodies which, in certain cases, are also authorised to issue instructions. They serve to carry out so-called state supervision and are located in ministries, special departments or other authorities. For data protection in Austria there is an Austrian Data Protection Authority; in Germany there is a separate data protection authority for each federal state.
Processor
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“processor” means a natural or legal person, public authority, agency or other body which processes personal data on behalf of the controller;
Explanation: As a company and website owner, we are responsible for all data that we process from you. In addition to controllers, there may also be so-called processors. This includes any company or person that processes personal data on our behalf. Processors can therefore, in addition to service providers such as tax advisors, also include hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
Supervisory authority concerned
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“supervisory authority concerned” means a supervisory authority which is concerned by the processing of personal data because
a)
the controller or processor is established on the territory of the Member State of that supervisory authority,
b)
data subjects residing in the Member State of that supervisory authority are substantially affected or likely to be substantially affected by the processing, or
c)
a complaint has been lodged with that supervisory authority;
Explanation: In Germany, each federal state has its own supervisory authority for data protection. So if your registered office (main establishment) is in Germany, the relevant supervisory authority of the federal state is generally your point of contact. In Austria, there is only one supervisory authority for data protection for the entire country.
Biometric data
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“biometric data” means personal data resulting from specific technical processing relating to the physical, physiological or behavioural characteristics of a natural person, which allow or confirm the unique identification of that natural person, such as facial images or dactyloscopic data;
Explanation: These are biological characteristics that are described by biometric data and from which personal data can be obtained using technical procedures. These include, for example, DNA, fingerprints, the geometry of various body parts, height, but also handwriting or the sound of a voice.
Filing system
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“filing system” means any structured set of personal data which are accessible according to specific criteria, whether centralised, decentralised or dispersed on a functional or geographical basis;
Explanation: Any organised storage of data on a computer storage medium is referred to as a “filing system”. If, for example, we store your name and e-mail address on a server for our newsletter, this data is located in a so-called “filing system”. Among the most important tasks of a “filing system” are the quick searching and finding of specific data and, of course, the secure storage of data.
Information society service
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“information society service” means a service as defined in point (b) of Article 1(1) of Directive (EU) 2015/1535 of the European Parliament and of the Council (19);
Explanation: Basically, the term “information society” refers to a society based on information and communication technologies. As a website visitor in particular, you are familiar with a wide variety of online services, and most online services count as “information society services”. A classic example of this is an online transaction, such as the purchase of goods via the internet.
Third party
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“third party” means a natural or legal person, public authority, agency or body other than the data subject, controller, processor and persons who, under the direct authority of the controller or processor, are authorised to process personal data;
Explanation: Here the GDPR basically only explains what a “third party” is not. In practice, a “third party” is anyone who also has an interest in the personal data but does not belong to the persons, authorities or bodies mentioned above. For example, a parent company can act as a “third party”. In this case, the subsidiary is the controller and the parent company is the “third party”. However, this does not mean that the parent company is automatically allowed to view, collect or store the personal data of the subsidiary.
Restriction of processing
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“restriction of processing” means the marking of stored personal data with the aim of limiting their processing in the future;
Explanation: It is one of your rights that you can request processors at any time to restrict your personal data from further processing operations. For this purpose, specific personal data such as your name, your date of birth or your address are marked in such a way that complete further processing is no longer possible. For example, you could restrict processing so that your data may no longer be used for personalised advertising.
Consent
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“consent” of the data subject means any freely given, specific, informed and unambiguous indication of the data subject’s wishes by which he or she, by a statement or by a clear affirmative action, signifies agreement to the processing of personal data relating to him or her;
Explanation: On websites, such consent is usually given via a cookie consent tool. You are surely familiar with this. Whenever you visit a website for the first time, you are usually asked via a banner whether you agree or consent to the data processing. In most cases, you can also make individual settings and thus decide for yourself which data processing you allow and which you do not. If you do not consent, no personal data may be processed from you. In principle, consent can of course also be given in writing, i.e. not via a tool.
Recipient
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“recipient” means a natural or legal person, public authority, agency or another body, to which the personal data are disclosed, whether a third party or not. However, public authorities which may receive personal data in the framework of a particular inquiry in accordance with Union or Member State law shall not be regarded as recipients; the processing of those data by those public authorities shall be in compliance with the applicable data protection rules according to the purposes of the processing;
Explanation: Every person and every company that receives personal data is considered a recipient. Thus, we and our processors are also so-called recipients. Only authorities that have an investigative mandate are not considered recipients.
Genetic data
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“genetic data” means personal data relating to the inherited or acquired genetic characteristics of a natural person which give unique information about the physiology or the health of that natural person and which result, in particular, from an analysis of a biological sample from the natural person in question;
Explanation: With a certain amount of effort, people can be identified through genetic data. That is why genetic data also falls into the category of personal data. Genetic data is obtained, for example, from blood or saliva samples.
Data concerning health
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“data concerning health” means personal data related to the physical or mental health of a natural person, including the provision of health care services, which reveal information about his or her health status;
Explanation: Health data therefore includes all stored information relating to your own health. These are often data that are also recorded in a patient file. These include, for example, which medications you use, X-ray images, your entire medical history or, as a rule, also your vaccination status.
Cross-border processing
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“cross-border processing” means either
a)
processing of personal data which takes place in the context of the activities of establishments in more than one Member State of a controller or processor in the Union where the controller or processor is established in more than one Member State, or
b)
processing of personal data which takes place in the context of the activities of a single establishment of a controller or processor in the Union but which substantially affects or is likely to substantially affect data subjects in more than one Member State;
Explanation: If, for example, a company or another organisation has establishments in Spain and in Croatia and personal data is processed in connection with the activities of the establishments, this constitutes “cross-border processing” of personal data. Even if the data is processed in only one country (as in this example, in Spain), but the effects on the data subject are also noticeable in another country, this is likewise referred to as “cross-border processing”.
Main establishment
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“main establishment” means
a)
as regards a controller with establishments in more than one Member State, the place of its central administration in the Union, unless the decisions on the purposes and means of the processing of personal data are taken in another establishment of the controller in the Union and the latter establishment has the power to have such decisions implemented, in which case the establishment having taken such decisions is to be considered to be the main establishment;
b)
as regards a processor with establishments in more than one Member State, the place of its central administration in the Union, or, if the processor has no central administration in the Union, the establishment of the processor in the Union where the main processing activities in the context of the activities of an establishment of the processor take place to the extent that the processor is subject to specific obligations under this Regulation;
Explanation: The company Google, for example, is an American company that also processes data in the USA, but its European main establishment is located in Ireland (Google Ireland Limited, Gordon House, Barrow Street Dublin 4, Irland). Legally speaking, Google Ireland Limited is therefore an independent company and is responsible for all Google products offered in the European Economic Area. In contrast to a main establishment, there are also branch offices; however, these do not act as legally independent establishments and must therefore also be distinguished from subsidiaries. A main establishment is therefore generally always the place where a company (commercial company) has its centre of operations.
International organisation
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“international organisation” means an organisation and its subordinate bodies governed by public international law, or any other body which is set up by, or on the basis of, an agreement between two or more countries.
Explanation: The best-known examples of international organisations are probably the European Union or the United Nations. The GDPR makes a distinction in connection with data transfers between third countries and international organisations. Within the EU, the transfer of personal data does not pose a problem, because all EU countries are bound by the requirements of the GDPR. By contrast, data transfers with third countries or international organisations are subject to certain conditions.
Relevant and reasoned objection
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“relevant and reasoned objection” means an objection to a draft decision as to whether there is an infringement of this Regulation, or whether envisaged action in relation to the controller or processor complies with this Regulation, which clearly demonstrates the significance of the risks posed by the draft decision as regards the fundamental rights and freedoms of data subjects and, where applicable, the free flow of personal data within the Union;
Explanation: If certain measures that we as controllers or our processors take are not in line with the GDPR, you can raise a so-called “relevant and reasoned objection”. In doing so, you must explain the significance of the risks with regard to your fundamental rights and freedoms and, where applicable, the free flow of your personal data within the EU.
Personal data
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“personal data” means any information relating to an identified or identifiable natural person (‘data subject’); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural or social identity of that natural person;
Explanation: Personal data is therefore all data that can identify you as a person. As a rule, this includes data such as:
- Name
- Address
- E-mail address
- Postal address
- Telephone number
- Date of birth
- Identification numbers such as social security number, tax identification number, identity card number or student registration number
- Bank data such as account number, credit information, account balances and much more.
According to the European Court of Justice (ECJ), your IP address is also personal data. Using your IP address, IT experts can determine at least the approximate location of your device and, subsequently, you as the connection owner. Therefore, storing an IP address also requires a legal basis within the meaning of the GDPR. There are also so-called “special categories” of personal data that are particularly worthy of protection. These include:
- racial and ethnic origin
- political opinions
- religious or philosophical beliefs
- trade union membership
- genetic data, such as data taken from blood or saliva samples
- biometric data (this is information on psychological, physical or behavioural characteristics that can identify a person).
health data - data concerning sexual orientation or sex life
Profiling
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“profiling” means any form of automated processing of personal data consisting of the use of personal data to evaluate certain personal aspects relating to a natural person, in particular to analyse or predict aspects concerning that natural person’s performance at work, economic situation, health, personal preferences, interests, reliability, behaviour, location or movements;
Explanation: In profiling, various pieces of information about a person are compiled in order to learn more about that person. On the web, profiling is often used for advertising purposes or for credit checks. Web or advertising analysis programs, for example, collect data about your behaviour and your interests on a website. This results in a special user profile, with the help of which advertising can be delivered specifically to a target group.
Pseudonymisation
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“pseudonymisation” means the processing of personal data in such a manner that the personal data can no longer be attributed to a specific data subject without the use of additional information, provided that such additional information is kept separately and is subject to technical and organisational measures to ensure that the personal data are not attributed to an identified or identifiable natural person;
Explanation: Our privacy policy frequently refers to pseudonymised data. Through pseudonymised data, you as a person can no longer be identified unless other information is added. However, you should not confuse pseudonymisation with anonymisation. With anonymisation, any personal reference is removed, so that it can really only be reconstructed with a disproportionately large technical effort.
Enterprise
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“enterprise” means a natural or legal person engaged in an economic activity, irrespective of its legal form, including partnerships or associations regularly engaged in an economic activity;
Explanation: We are, for example, an enterprise and also carry out an economic activity via our website by offering and selling services and/or products. For every enterprise, the formal characteristic is its legal form, such as a GmbH (limited liability company) or an AG (public limited company).
Group of undertakings
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“group of undertakings” means a controlling undertaking and its controlled undertakings;
Explanation: A “group of undertakings” therefore exists when several companies join together and are legally and financially connected with one another, but there is nevertheless a central, overarching company. For example, Instagram, WhatsApp, Oculus VR or Facebook are largely independent companies, but they are all subject to the parent company Meta Platforms, Inc.
Controller
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“controller” means the natural or legal person, public authority, agency or other body which, alone or jointly with others, determines the purposes and means of the processing of personal data; where the purposes and means of such processing are determined by Union or Member State law, the controller or the specific criteria for its nomination may be provided for by Union or Member State law;
Explanation: In our case, we are responsible for the processing of your personal data and are therefore the “controller”. If we pass on collected data to other service providers for processing, these are “processors”. For this purpose, a “data processing agreement (DPA)” must be signed.
Processing
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“processing” means any operation or set of operations which is performed on personal data or on sets of personal data, whether or not by automated means, such as collection, recording, organisation, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, dissemination or otherwise making available, alignment or combination, restriction, erasure or destruction;
Note: When we speak of processing in our privacy policy, we mean any type of data processing. As mentioned above in the original GDPR definition, this includes not only the collection but also the storage and processing of data.
Binding corporate rules
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“binding corporate rules” means personal data protection policies which are adhered to by a controller or processor established on the territory of a Member State for transfers or a set of transfers of personal data to a controller or processor in one or more third countries within a group of undertakings, or group of enterprises engaged in a joint economic activity;
Explanation: You may have heard or read the term “Binding Corporate Rules” many times before. This is the term that most often appears when it comes to binding internal data protection rules. Especially for companies (such as Google) that process data in third countries, such internal rules are advisable, through which a company, so to speak, commits itself to complying with data protection regulations. These rules govern the handling of personal data that is transferred to third countries and also processed there.
Personal data breach
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“personal data breach” means a breach of security leading to the accidental or unlawful destruction, loss, alteration, unauthorised disclosure of, or access to, personal data transmitted, stored or otherwise processed;
Explanation: For example, a “personal data breach” can occur in the event of a data leak, i.e. a technical problem or a cyberattack. If the breach results in a risk to the rights and freedoms of natural persons, the controller must report the incident immediately to the competent supervisory authority. In addition, the data subjects must also be informed if the breach poses a high risk to the rights and freedoms of natural persons.
Representative
Definition according to Article 4 of the GDPR
For the purposes of this Regulation:
“representative” means a natural or legal person established in the Union who, designated by the controller or processor in writing pursuant to Article 27, represents the controller or processor with regard to their respective obligations under this Regulation;
Explanation: A “representative” can therefore be any person who has been appointed in writing by us (controller) or by one of our service providers (processor). Companies outside the EU that process data of EU citizens must designate a representative within the EU. If, for example, a web analytics provider has its main establishment in the USA, it must appoint a “representative” within the European Union who represents the obligations relating to data processing.
Closing remarks
Congratulations! If you are reading these lines, you have really “battled” your way through our entire privacy policy, or at least scrolled down this far. As you can see from the scope of our privacy policy, we take the protection of your personal data anything but lightly.
It is important to us to inform you about the processing of personal data to the best of our knowledge and belief. In doing so, we want not only to tell you which data is processed, but also to explain the reasons for using various software programs. As a rule, privacy policies sound very technical and legalistic. However, since most of you are not web developers or lawyers, we also wanted to take a different approach linguistically and explain the facts in simple and clear language. Of course, this is not always possible due to the subject matter. Therefore, the most important terms are explained in more detail at the end of the privacy policy.
If you have any questions about data protection on our website, please do not hesitate to contact us or the responsible body. We wish you a pleasant time and hope to welcome you back to our website soon.
All texts are protected by copyright.
Source: Created with the Privacy Policy Generator Austria by AdSimple